
Top 6 Most Common Financial Services Cybersecurity Gaps We See
Financial services cybersecurity often looks stronger on paper than it is in practice. Banks and financial institutions may have firewalls, EDR, MFA and SIEM in place, yet gaps can remain across privileged access, phishing, third-party accounts, data access and incident response. These gaps are easy to miss because security teams are managing complex environments, […]
How to Build a SOC Monitoring Program for CBUAE-Regulated Institutions
To build a security monitoring program for a CBUAE-regulated institution, start with SOC monitoring that continuously detects, investigates, and escalates threats. That means knowing what to monitor, which alerts matter, who responds and how you prove the process works. This guide shows how to turn CBUAE’s cybersecurity expectations into a practical monitoring program that works […]
In-House vs Managed Security Operations Center: What to Pick?
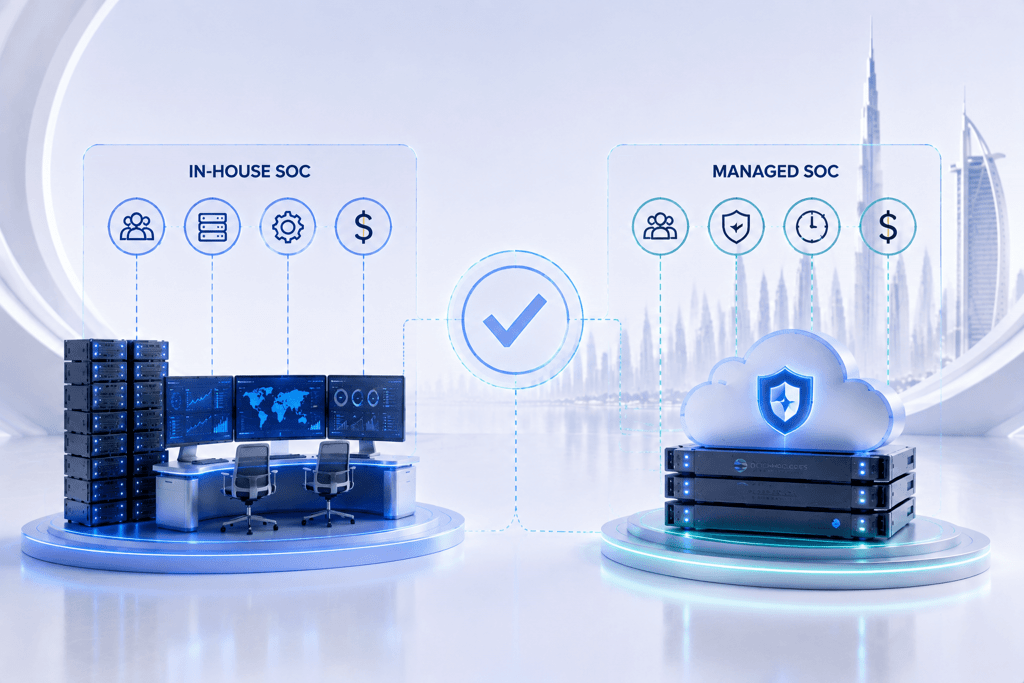
If you have the people, budget, and security maturity to operate 24×7 monitoring internally, an in-house security operations center gives you greater control. For most mid-market businesses in the UAE without that capacity, SOC as a Service is the more practical option because you get continuous monitoring, security expertise, and established processes without building the […]
EDR vs XDR: What’s the Difference and Which Does Your Business Need?
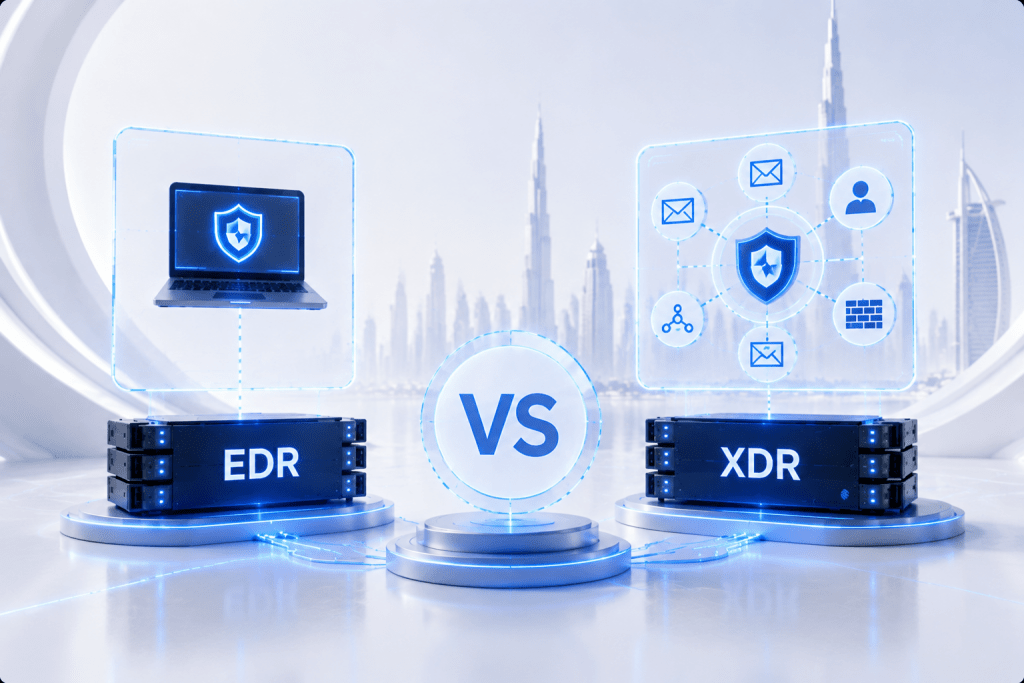
If you already have EDR, do you really need XDR? EDR vs XDR comes down to how much of an attack you can actually see. Your endpoint might flag suspicious activity, but what happened before that? Was an employee’s account compromised? Did a phishing email open the door? Did the attacker move through a […]