We’ve previously written about the major UAE cybersecurity attacks in relation to financial services and the healthcare industries.
The one underlying cause that comes out from some of those is the fragmentation of tools, or the lack of monitoring, or the fact that alerts are getting generated, but there is no set process to manage them and take appropriate action in the least possible time.
A business with 200-1,000 endpoints may already have EDR, firewalls, Microsoft 365 security and even SIEM and other tools.
Most of the times, their security posture isn’t still improving with time. That’s because tools need the right tuning and the configurations to actually work in your favor.
Additionally, having the tools doesn’t guarantee that the threats or the alerts will be continuously monitored or proper response to the incidents will be taken.
That’s where a good managed Security Operations Center (SOC) for UAE comes in. Emirates like Dubai, Abu Dhabi, Ajman, Ras Al Khaimah and others are heavily growing business hubs, and managed SOC for businesses here is quite crucial.
A managed SOC provides continuous security monitoring, threat investigation and incident response without requiring businesses to build and staff their own security operations center.
However, not every SOC provider delivers the same level of support. Some focus on monitoring and escalating alerts. Others provide fully managed security operations, including L1–L3 analysts, threat hunting, detection tuning and hands-on containment.
This guide compares seven managed SOC providers serving UAE businesses with approximately 200–1,000 endpoints. We examine their capabilities, specialist resources, technology compatibility, and service limitations to help you identify the right fit for your security requirements.
How We Selected These Managed SOC Providers in UAE
We reviewed publicly available service information from providers offering outsourced security operations to businesses in the UAE.
Our selection focused on:
- SOC operations: Continuous monitoring, investigation and incident response rather than SIEM implementation alone.
- SMB suitability: Services relevant to organizations with 200–1,000 endpoints and limited internal security resources.
- Analyst capabilities: L1–L3 expertise, escalation procedures and access to specialist investigators.
- Technology compatibility: Support for existing security products, SIEM platforms, and cloud environments.
- Delivery transparency: Published service tiers, monitoring hours, log limits and incident response responsibilities
This is not a ranking from best to worst. These providers are included because their different delivery models may suit different business requirements.
The comparison reflects publicly described services, and, for DC Technologies, additional information provided by its team.
Actual staffing, response performance, and commercial terms should be verified before selecting a provider.
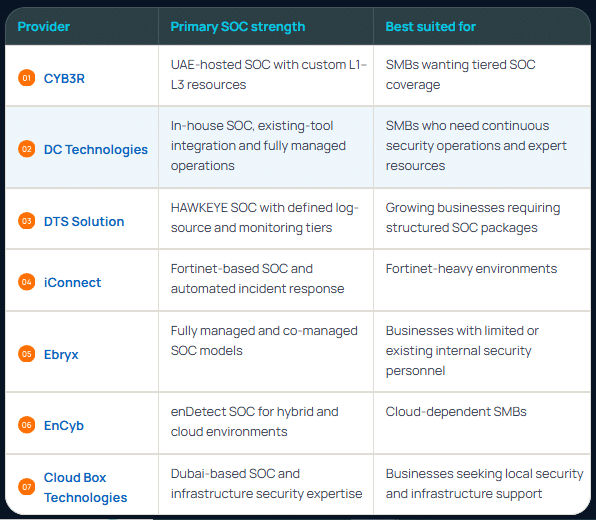
Quick Comparison of 7 Managed SOC Providers in UAE
Provider
Primary SOC strength
Best suited for
- CYB3R
UAE-hosted SOC with custom L1–L3 resources
SMBs wanting tiered SOC coverage
- DC Technologies
In-house SOC, existing-tool integration and fully managed operations
SMBs who need continuous security operations and expert resources
- DTS Solution
HAWKEYE SOC with defined log-source and monitoring tiers
Growing businesses requiring structured SOC packages
- iConnect
Fortinet-based SOC and automated incident response
Fortinet-heavy environments
- Ebryx
Fully managed and co-managed SOC models
Businesses with limited or existing internal security personnel
- EnCyb
enDetect SOC for hybrid and cloud environments
Cloud-dependent SMBs
- Cloud Box Technologies
Dubai-based SOC and infrastructure security expertise
Businesses seeking local security and infrastructure support
1. CYB3R
Best for: UAE SMBs looking for scalable SOC services with the option to obtain dedicated L1–L3 security resources.
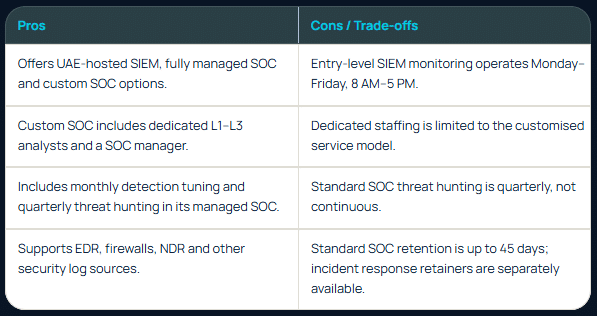
CYB3R offers a UAE-hosted Security Operations Centre through three models: SIEM as a Service, CYB3R SOC and Custom SOC.
Its fully managed offering includes investigation of high and critical alerts, detection-rule tuning, threat intelligence, SOAR automation and quarterly threat hunting.
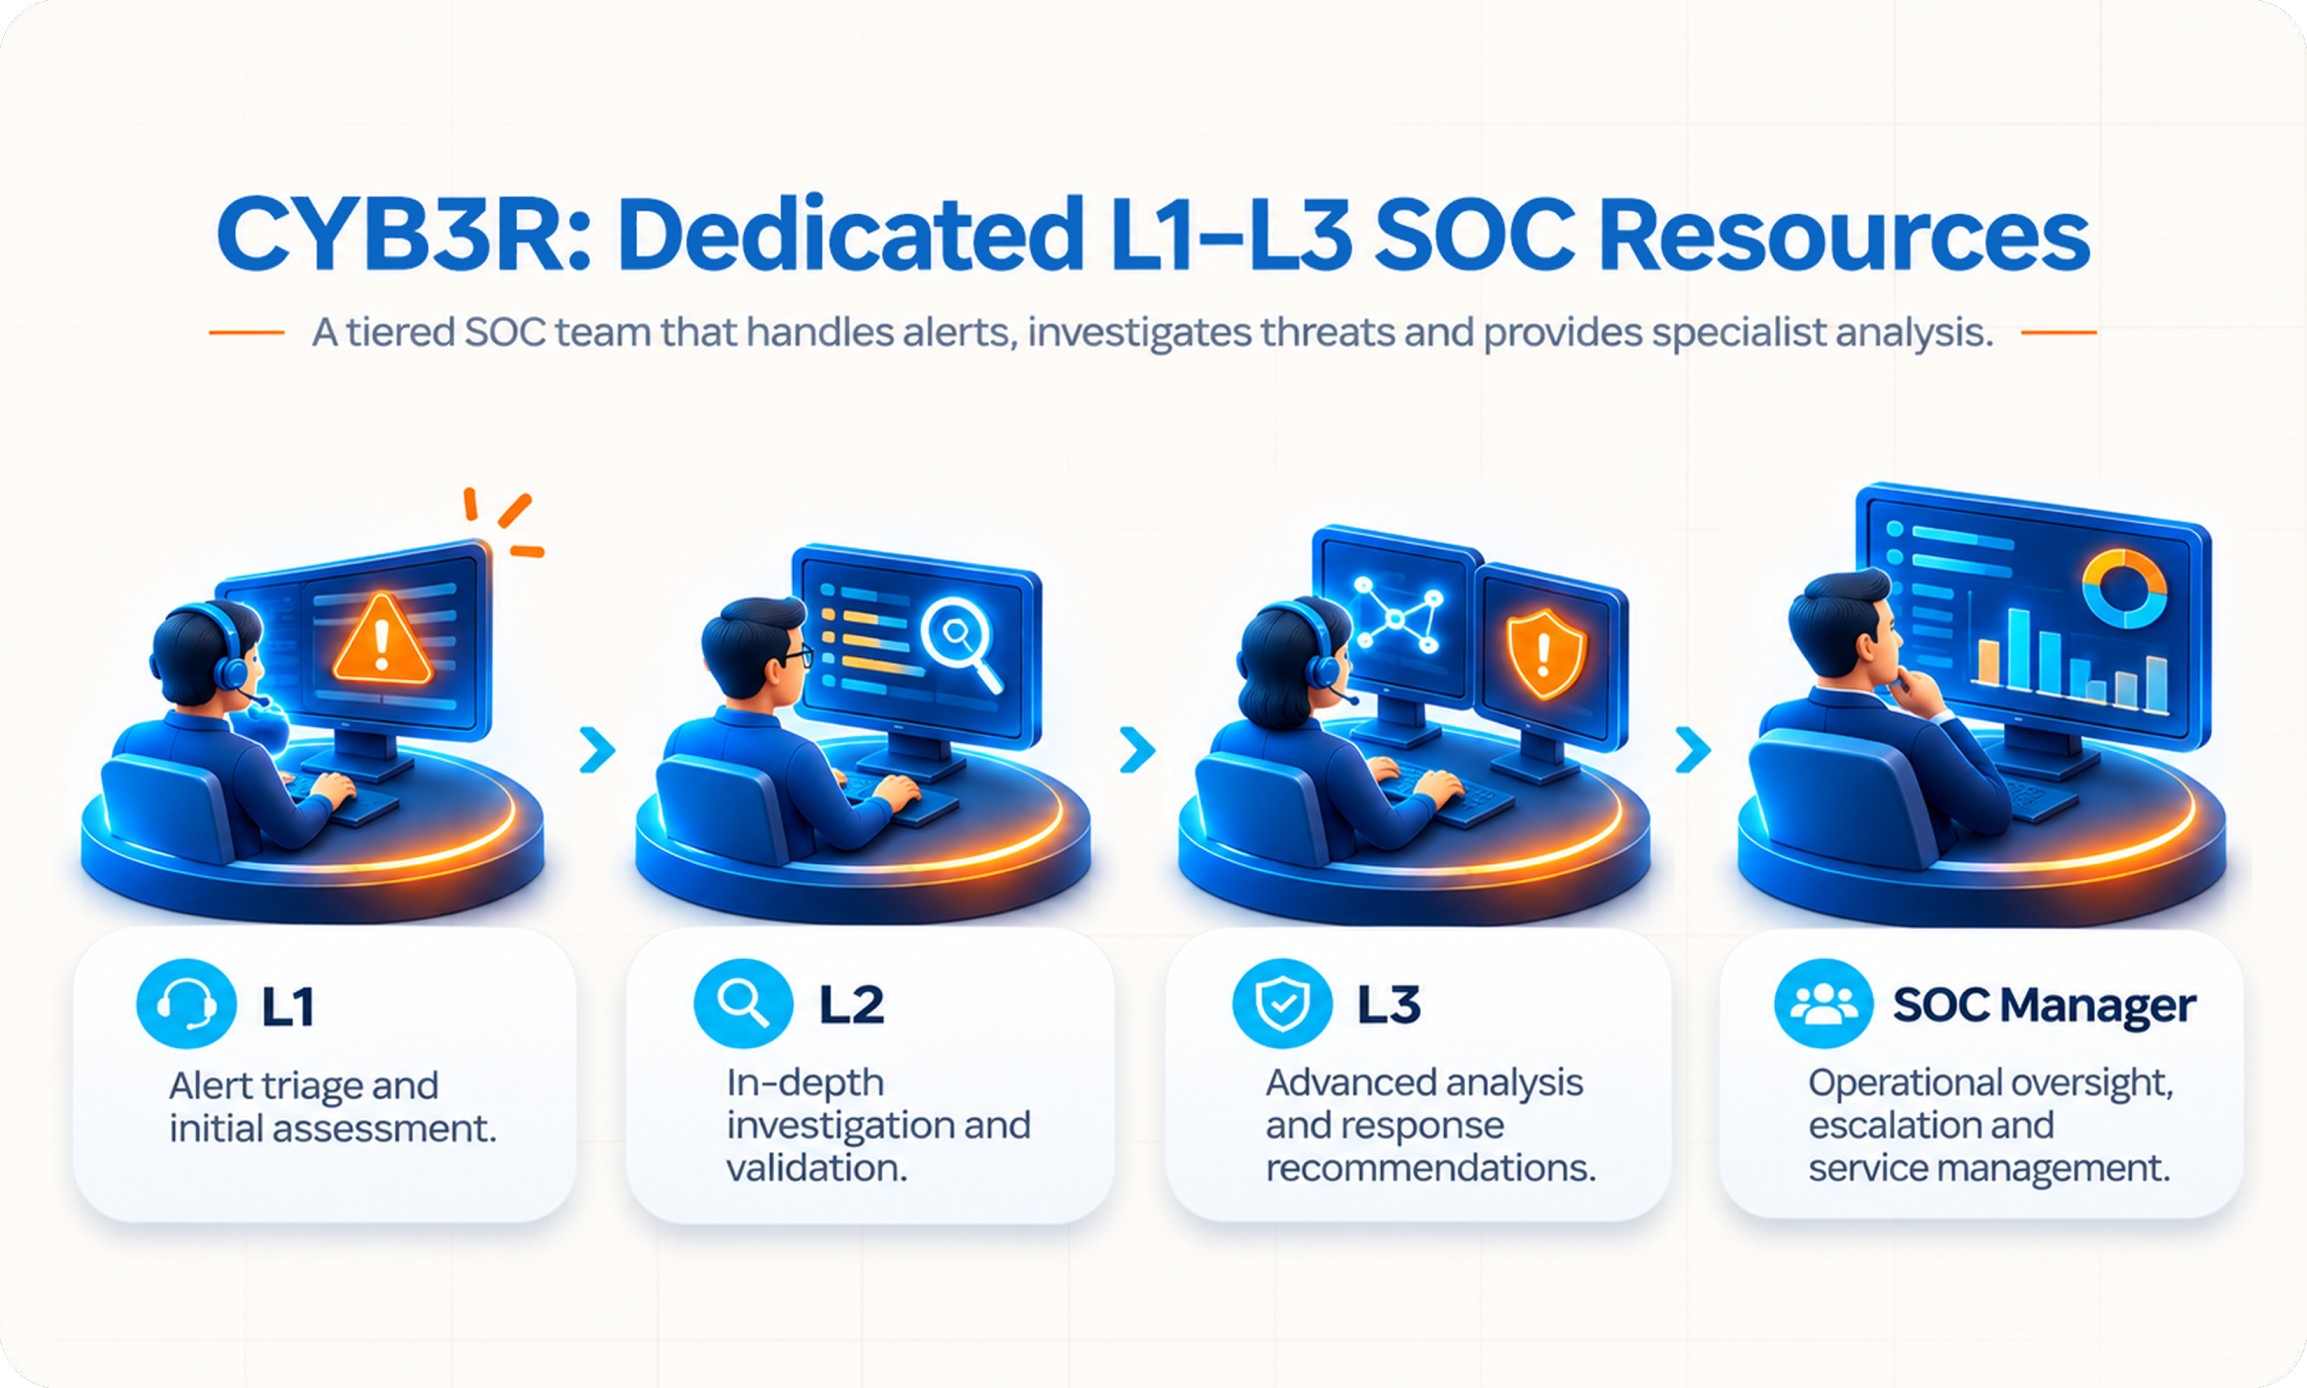
The custom offering adds dedicated L1–L3 analysts, a SOC manager and tailored incident management. This gives SMBs different levels of support depending on their monitoring requirements, internal capabilities and budget.
However, customers need to distinguish its basic SIEM monitoring service from its fully managed SOC.
Pros
Cons / Trade-offs
- Offers UAE-hosted SIEM, fully managed SOC and custom SOC options.
Entry-level SIEM monitoring operates Monday–Friday, 8 AM–5 PM.
- Custom SOC includes dedicated L1–L3 analysts and a SOC manager.
Dedicated staffing is limited to the customised service model.
- Includes monthly detection tuning and quarterly threat hunting in its managed SOC.
Standard SOC threat hunting is quarterly, not continuous.
- Supports EDR, firewalls, NDR and other security log sources.
Standard SOC retention is up to 45 days; incident response retainers are separately available.
2. DC Technologies
Best for: UAE SMBs requiring continuous security operations across their existing technology investments.
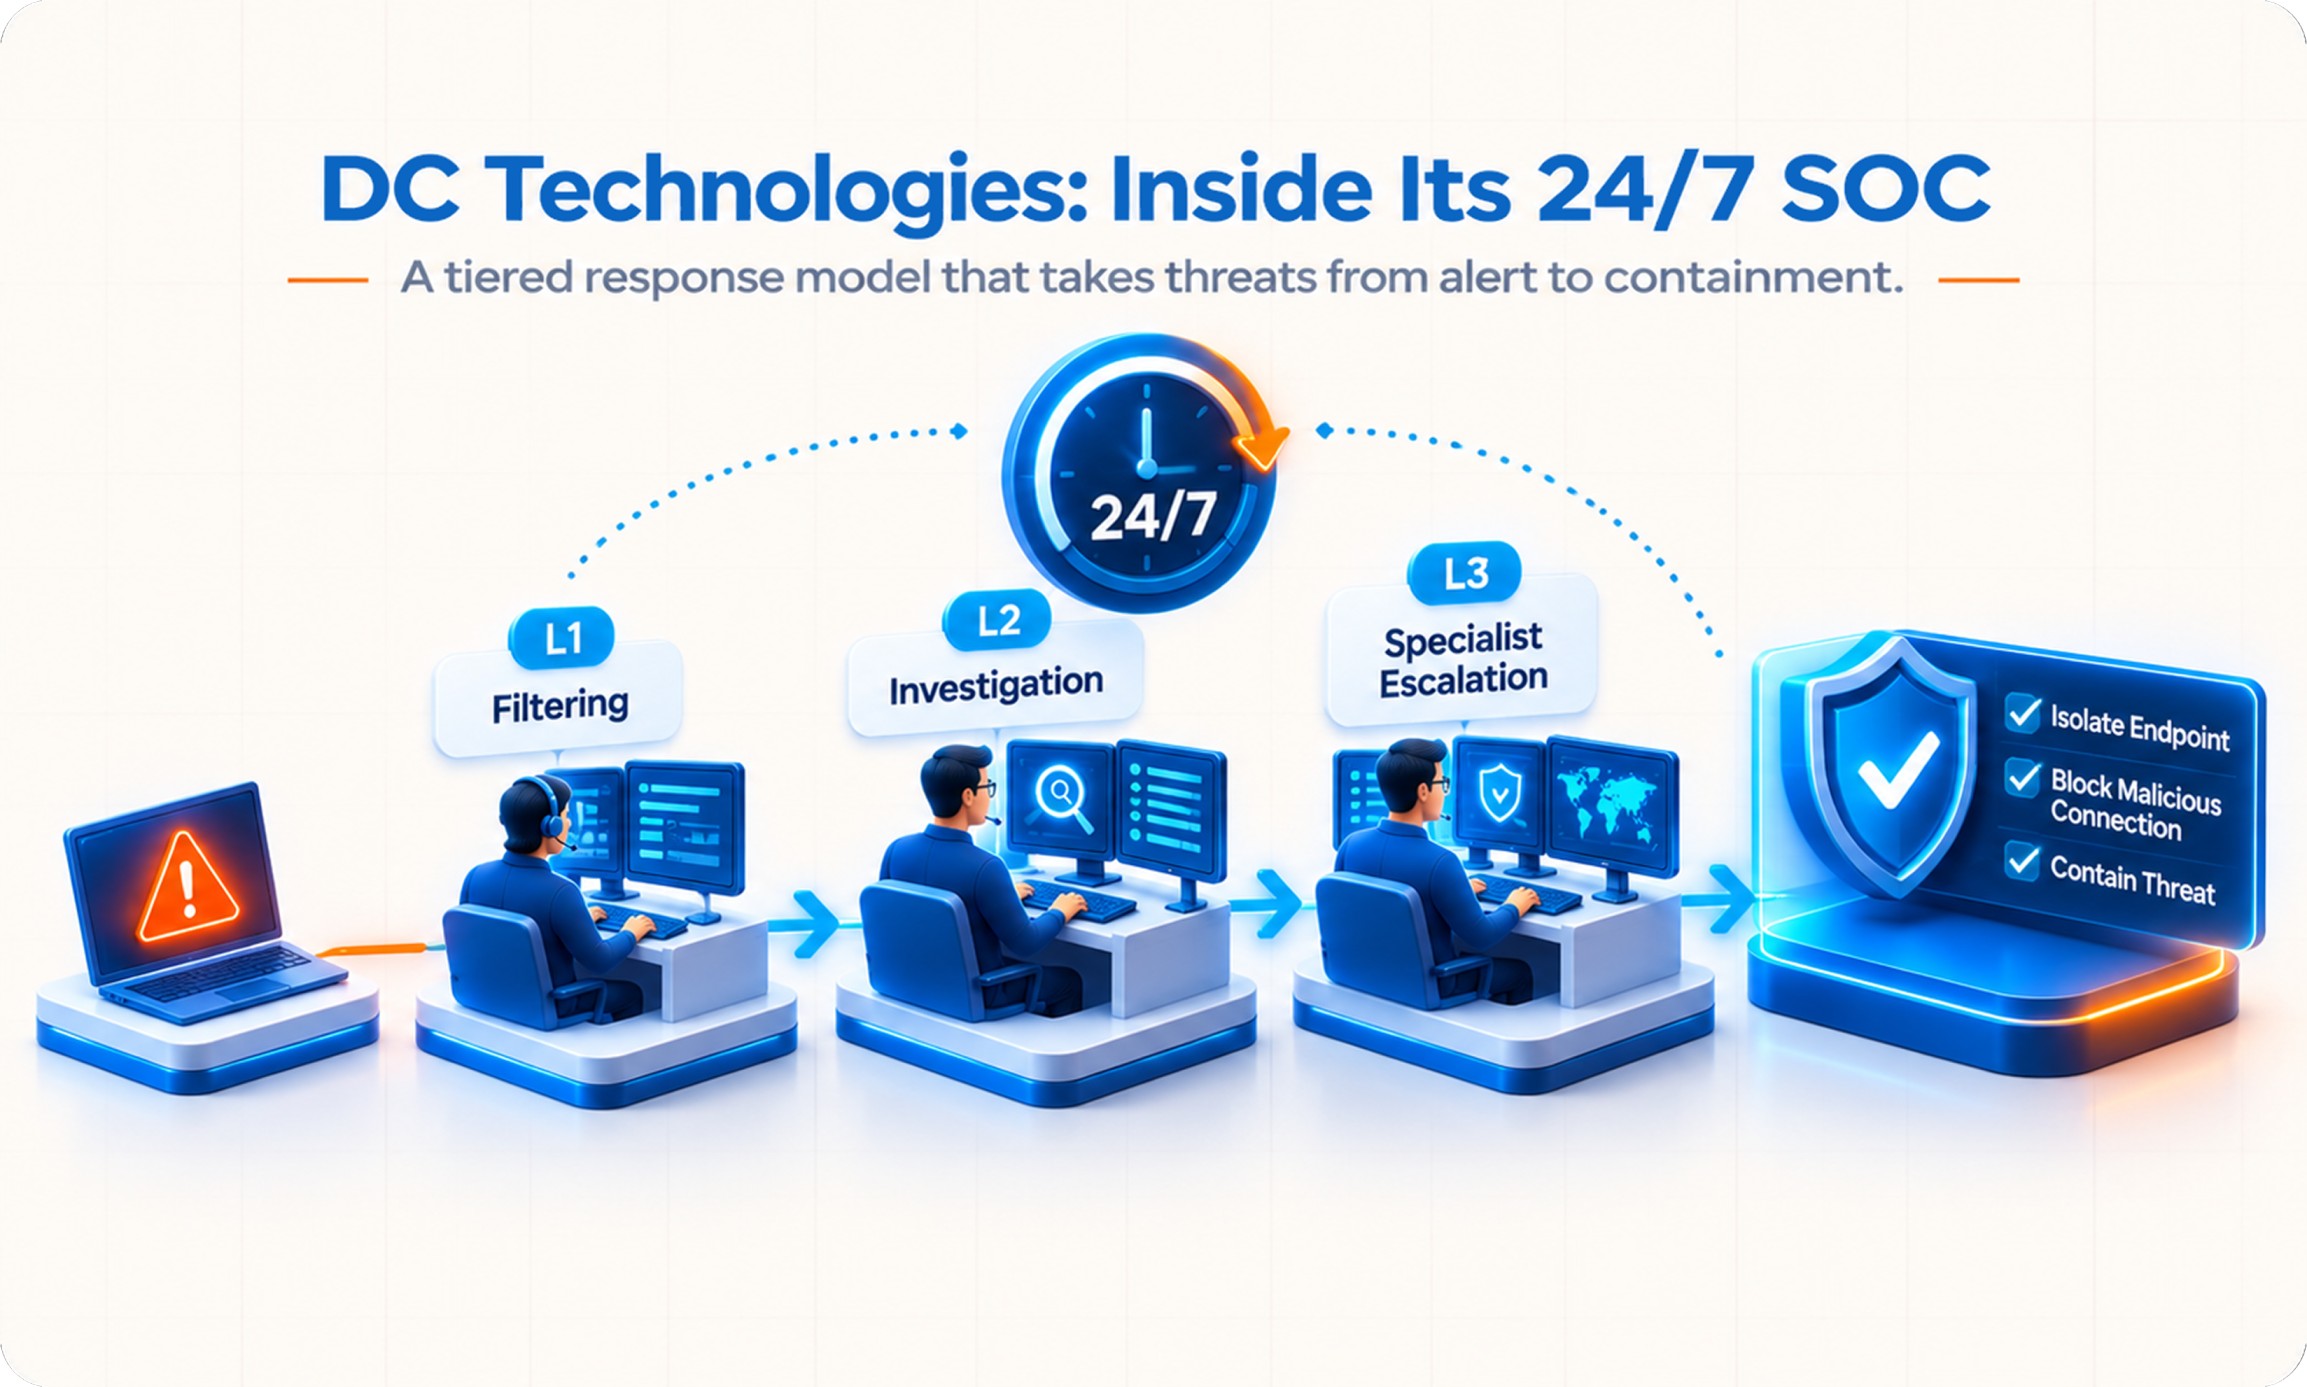
DC Technologies provides managed SOC services for UAE businesses that need 24/7 monitoring and incident response without building an internal security operations team.
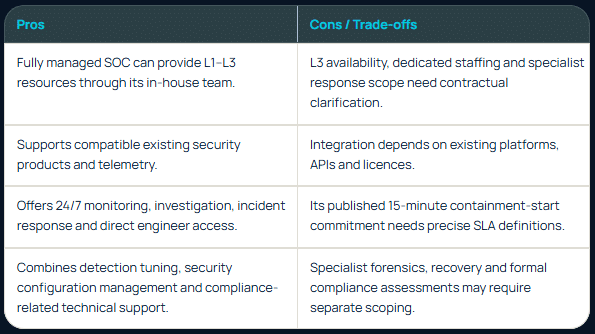
Its in-house analysts handle alert triage, threat investigation and response, with a fully managed L1–L3 model available for scoping.
Beyond monitoring, DC Technologies helps customers configure and tune compatible security products to operate according to established policies.
Its managed infrastructure experience and compliance knowledge also support technical security controls and incident coordination.
For businesses already using EDR, firewalls, Microsoft 365 security and other platforms, the approach reduces the need to replace existing investments simply to obtain managed security operations.
Pros
Cons / Trade-offs
- Fully managed SOC can provide L1–L3 resources through its in-house team.
L3 availability, dedicated staffing and specialist response scope need contractual clarification.
- Supports compatible existing security products and telemetry.
Integration depends on existing platforms, APIs and licences.
- Offers 24/7 monitoring, investigation, incident response and direct engineer access.
Its published 15-minute containment-start commitment needs precise SLA definitions.
- Combines detection tuning, security configuration management and compliance-related technical support.
Specialist forensics, recovery and formal compliance assessments may require separate scoping.
See how DC Tech's Managed SOC works for your environment?
3. DTS Solution (HAWKEYE)
Best for: UAE SMBs looking for defined SOC service tiers with different monitoring hours and log-source capacities.
DTS Solution operates HAWKEYE, a managed cybersecurity operations service with SIEM, XDR, threat intelligence, investigation and threat hunting capabilities.
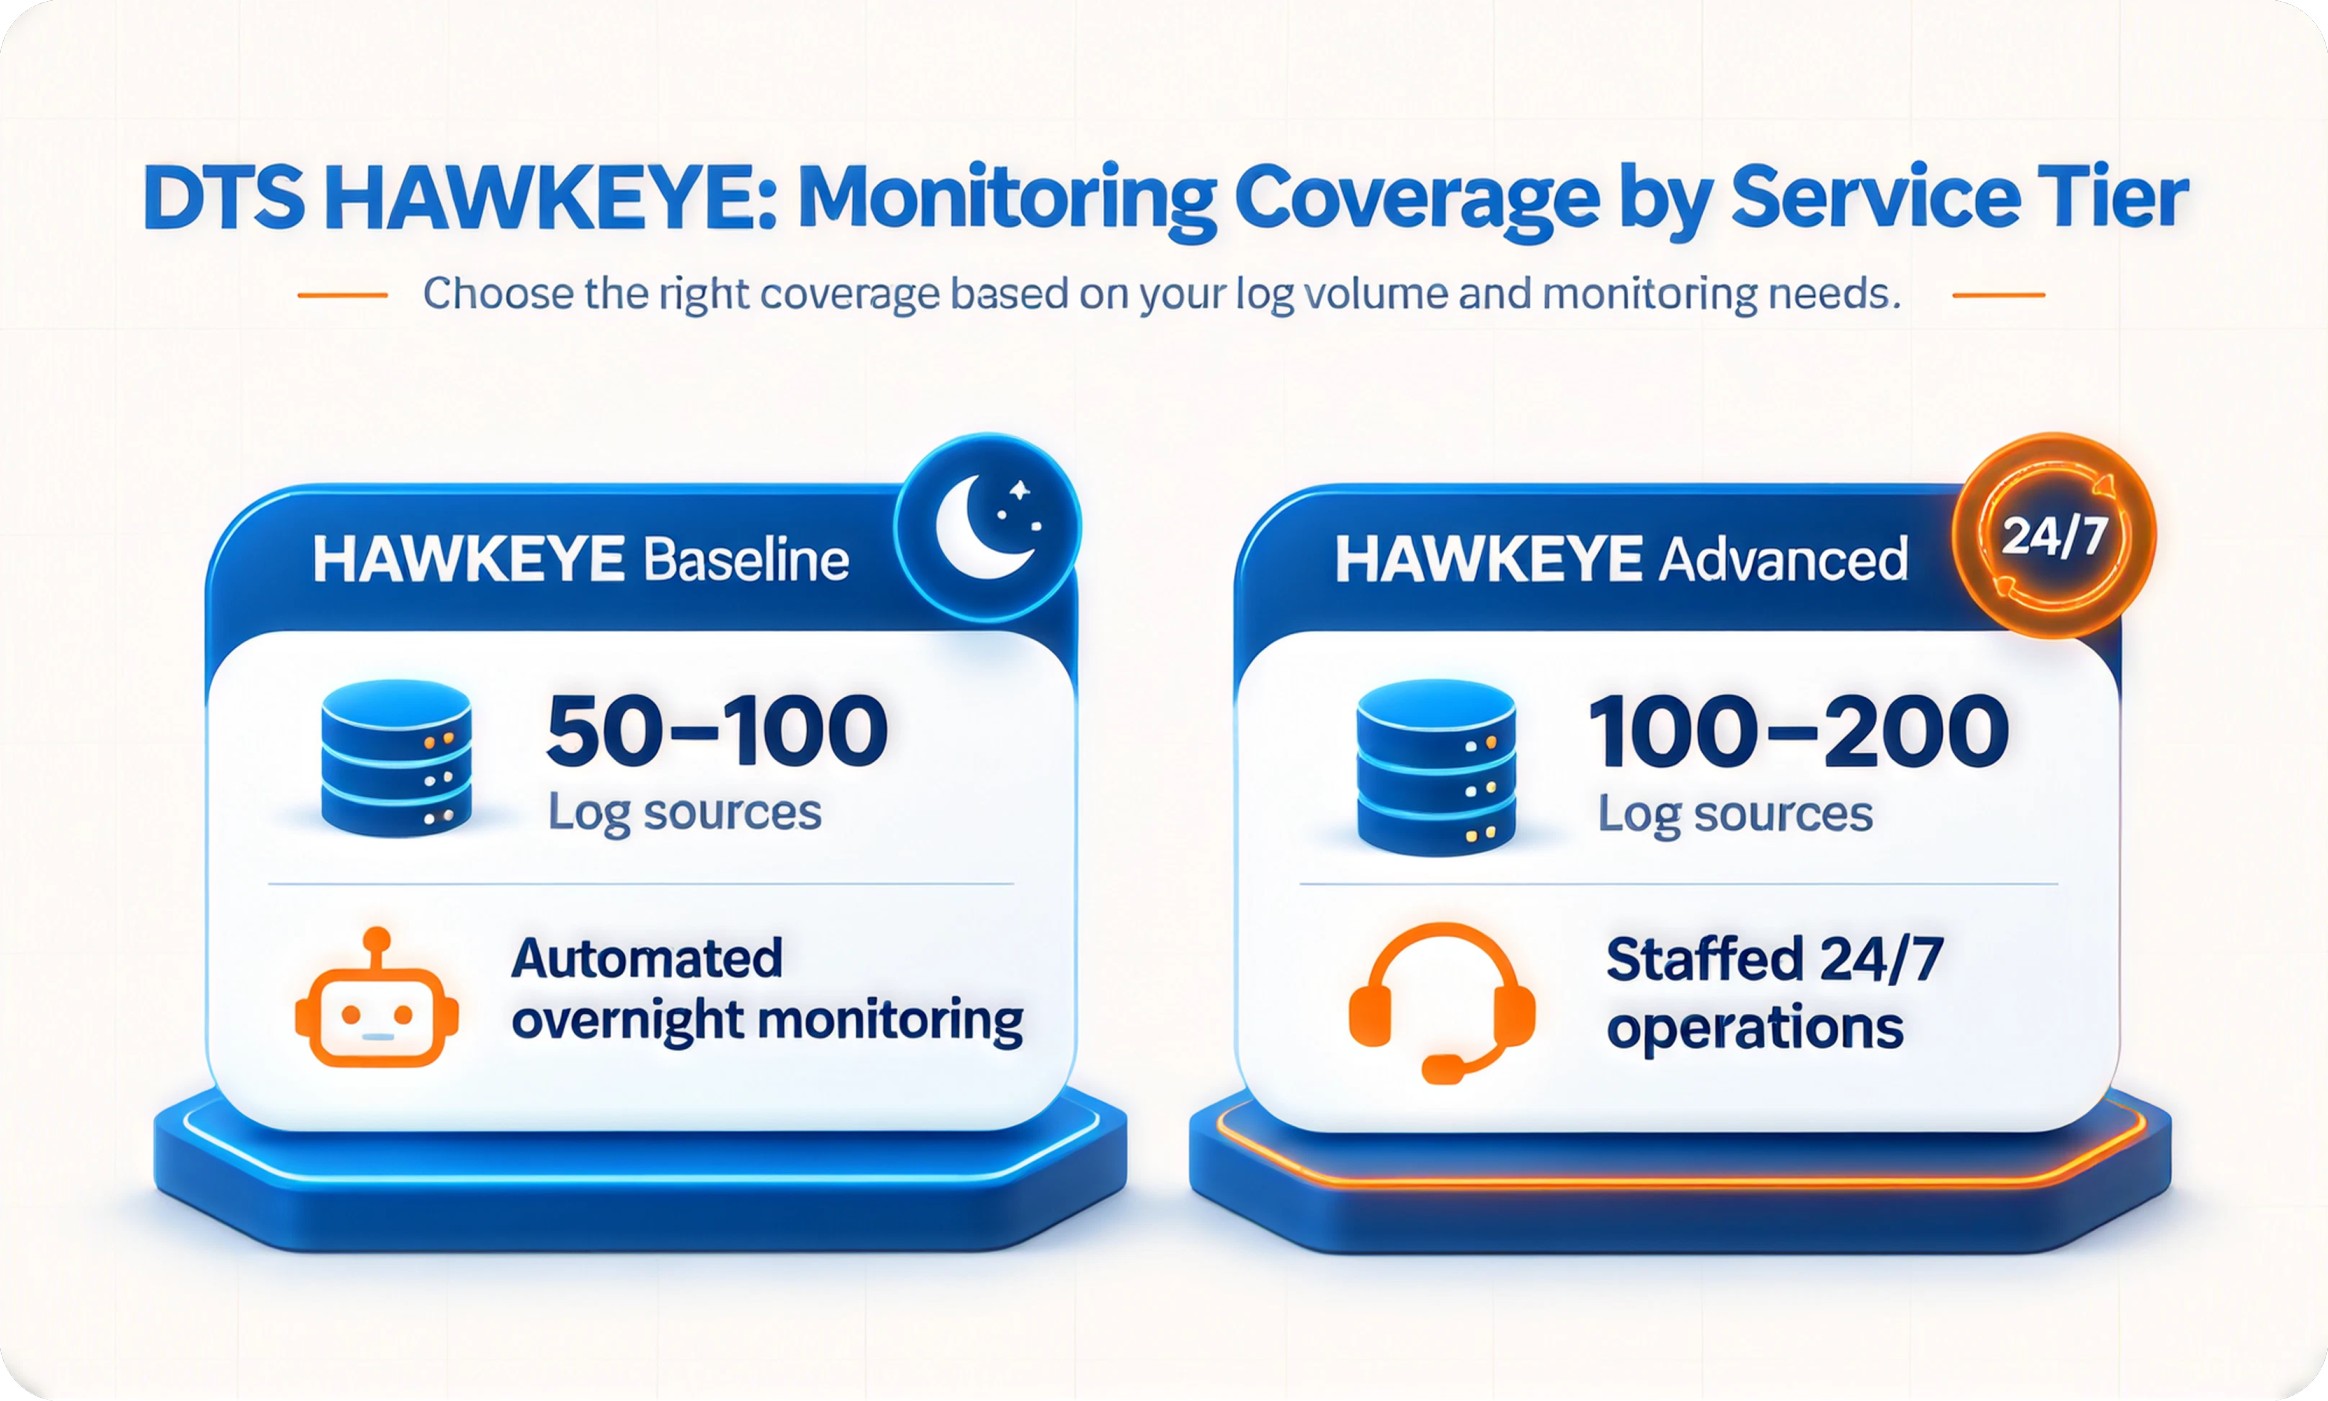
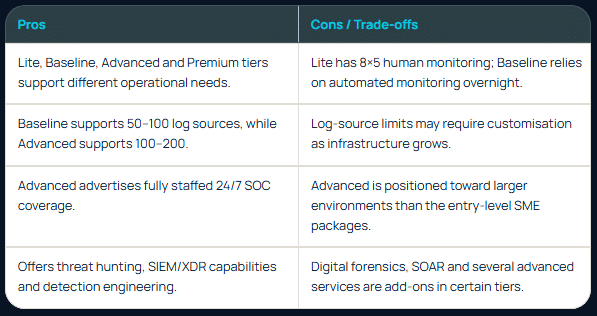
HAWKEYE offers Lite, Baseline, Advanced and Premium packages. Lite focuses on perimeter monitoring, while Baseline extends coverage to internal networks and critical systems.
Advanced adds continuously staffed 24/7 operations and broader log-source capacity. DTS also offers detection engineering and specialist cyber response services.
Its published packages make it easier to compare operational coverage, but buyers must distinguish automated overnight monitoring from round-the-clock analyst availability.
Pros
Cons / Trade-offs
- Lite, Baseline, Advanced and Premium tiers support different operational needs.
Lite has 8×5 human monitoring; Baseline relies on automated monitoring overnight.
- Baseline supports 50–100 log sources, while Advanced supports 100–200.
Log-source limits may require customisation as infrastructure grows.
- Advanced advertises fully staffed 24/7 SOC coverage.
Advanced is positioned toward larger environments than the entry-level SME packages.
- Offers threat hunting, SIEM/XDR capabilities and detection engineering.
Digital forensics, SOAR and several advanced services are add-ons in certain tiers.
4. iConnect IT Business Solutions
Best for: UAE businesses with Fortinet infrastructure seeking managed SOC and automated response capabilities.
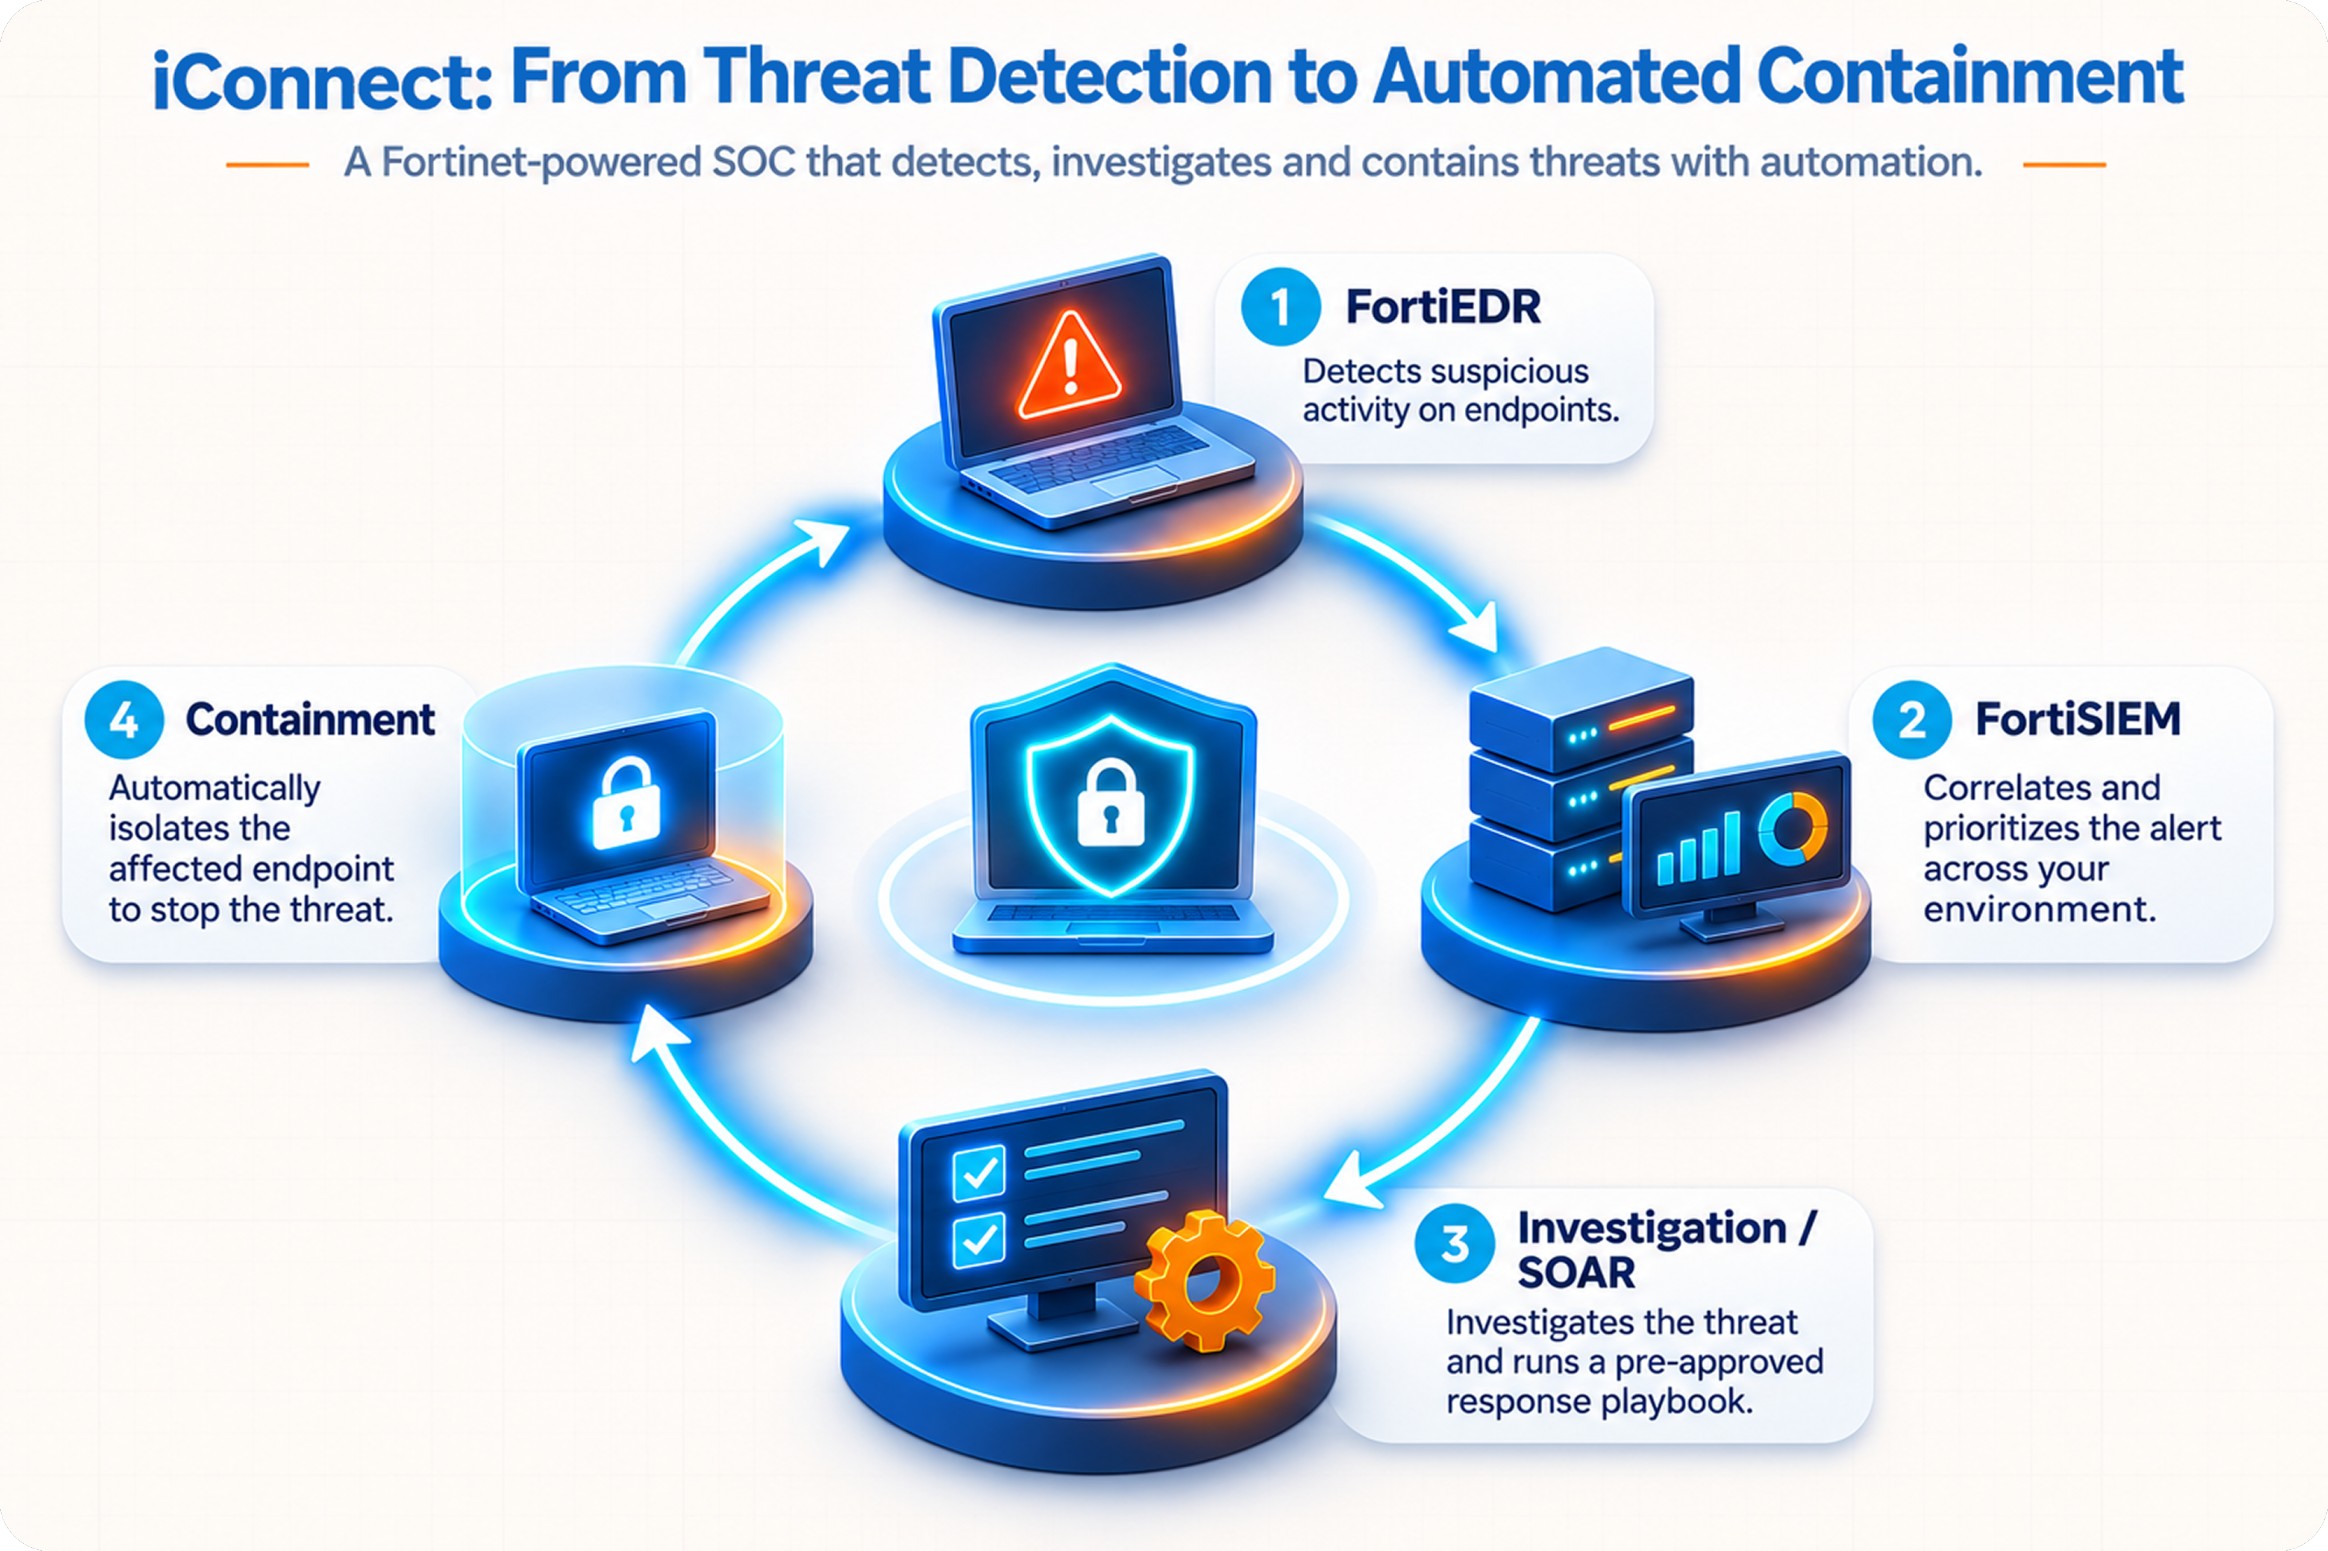
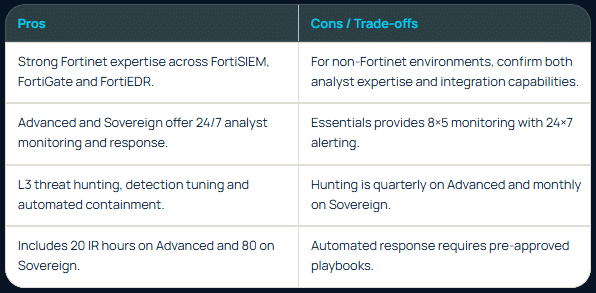
iConnect operates a Dubai-based SOC centred on the Fortinet Security Fabric. Its service combines FortiSIEM, endpoint and network detection, L3 threat hunting, detection engineering and SOAR-based containment.
The provider offers Essentials, Advanced and Sovereign tiers, with different monitoring hours and response capabilities.
Its Fortinet specialization is particularly relevant to businesses already using FortiGate, FortiEDR or other Fortinet products, although third-party integrations are also supported.
Pros
Cons / Trade-offs
- Strong Fortinet expertise across FortiSIEM, FortiGate and FortiEDR.
For non-Fortinet environments, confirm both analyst expertise and integration capabilities.
- Advanced and Sovereign offer 24/7 analyst monitoring and response.
Essentials provides 8×5 monitoring with 24×7 alerting.
- L3 threat hunting, detection tuning and automated containment.
Hunting is quarterly on Advanced and monthly on Sovereign.
- Includes 20 IR hours on Advanced and 80 on Sovereign.
Automated response requires pre-approved playbooks.
5. Ebryx
Best for: SMBs seeking a fully outsourced SOC or a co-managed arrangement that extends their existing security team.
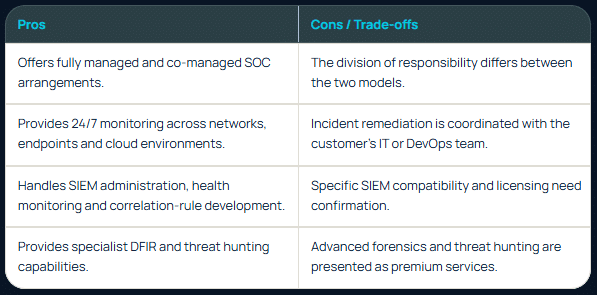
Ebryx offers managed security operations with 24/7 monitoring, incident investigation, SIEM management and vulnerability management.
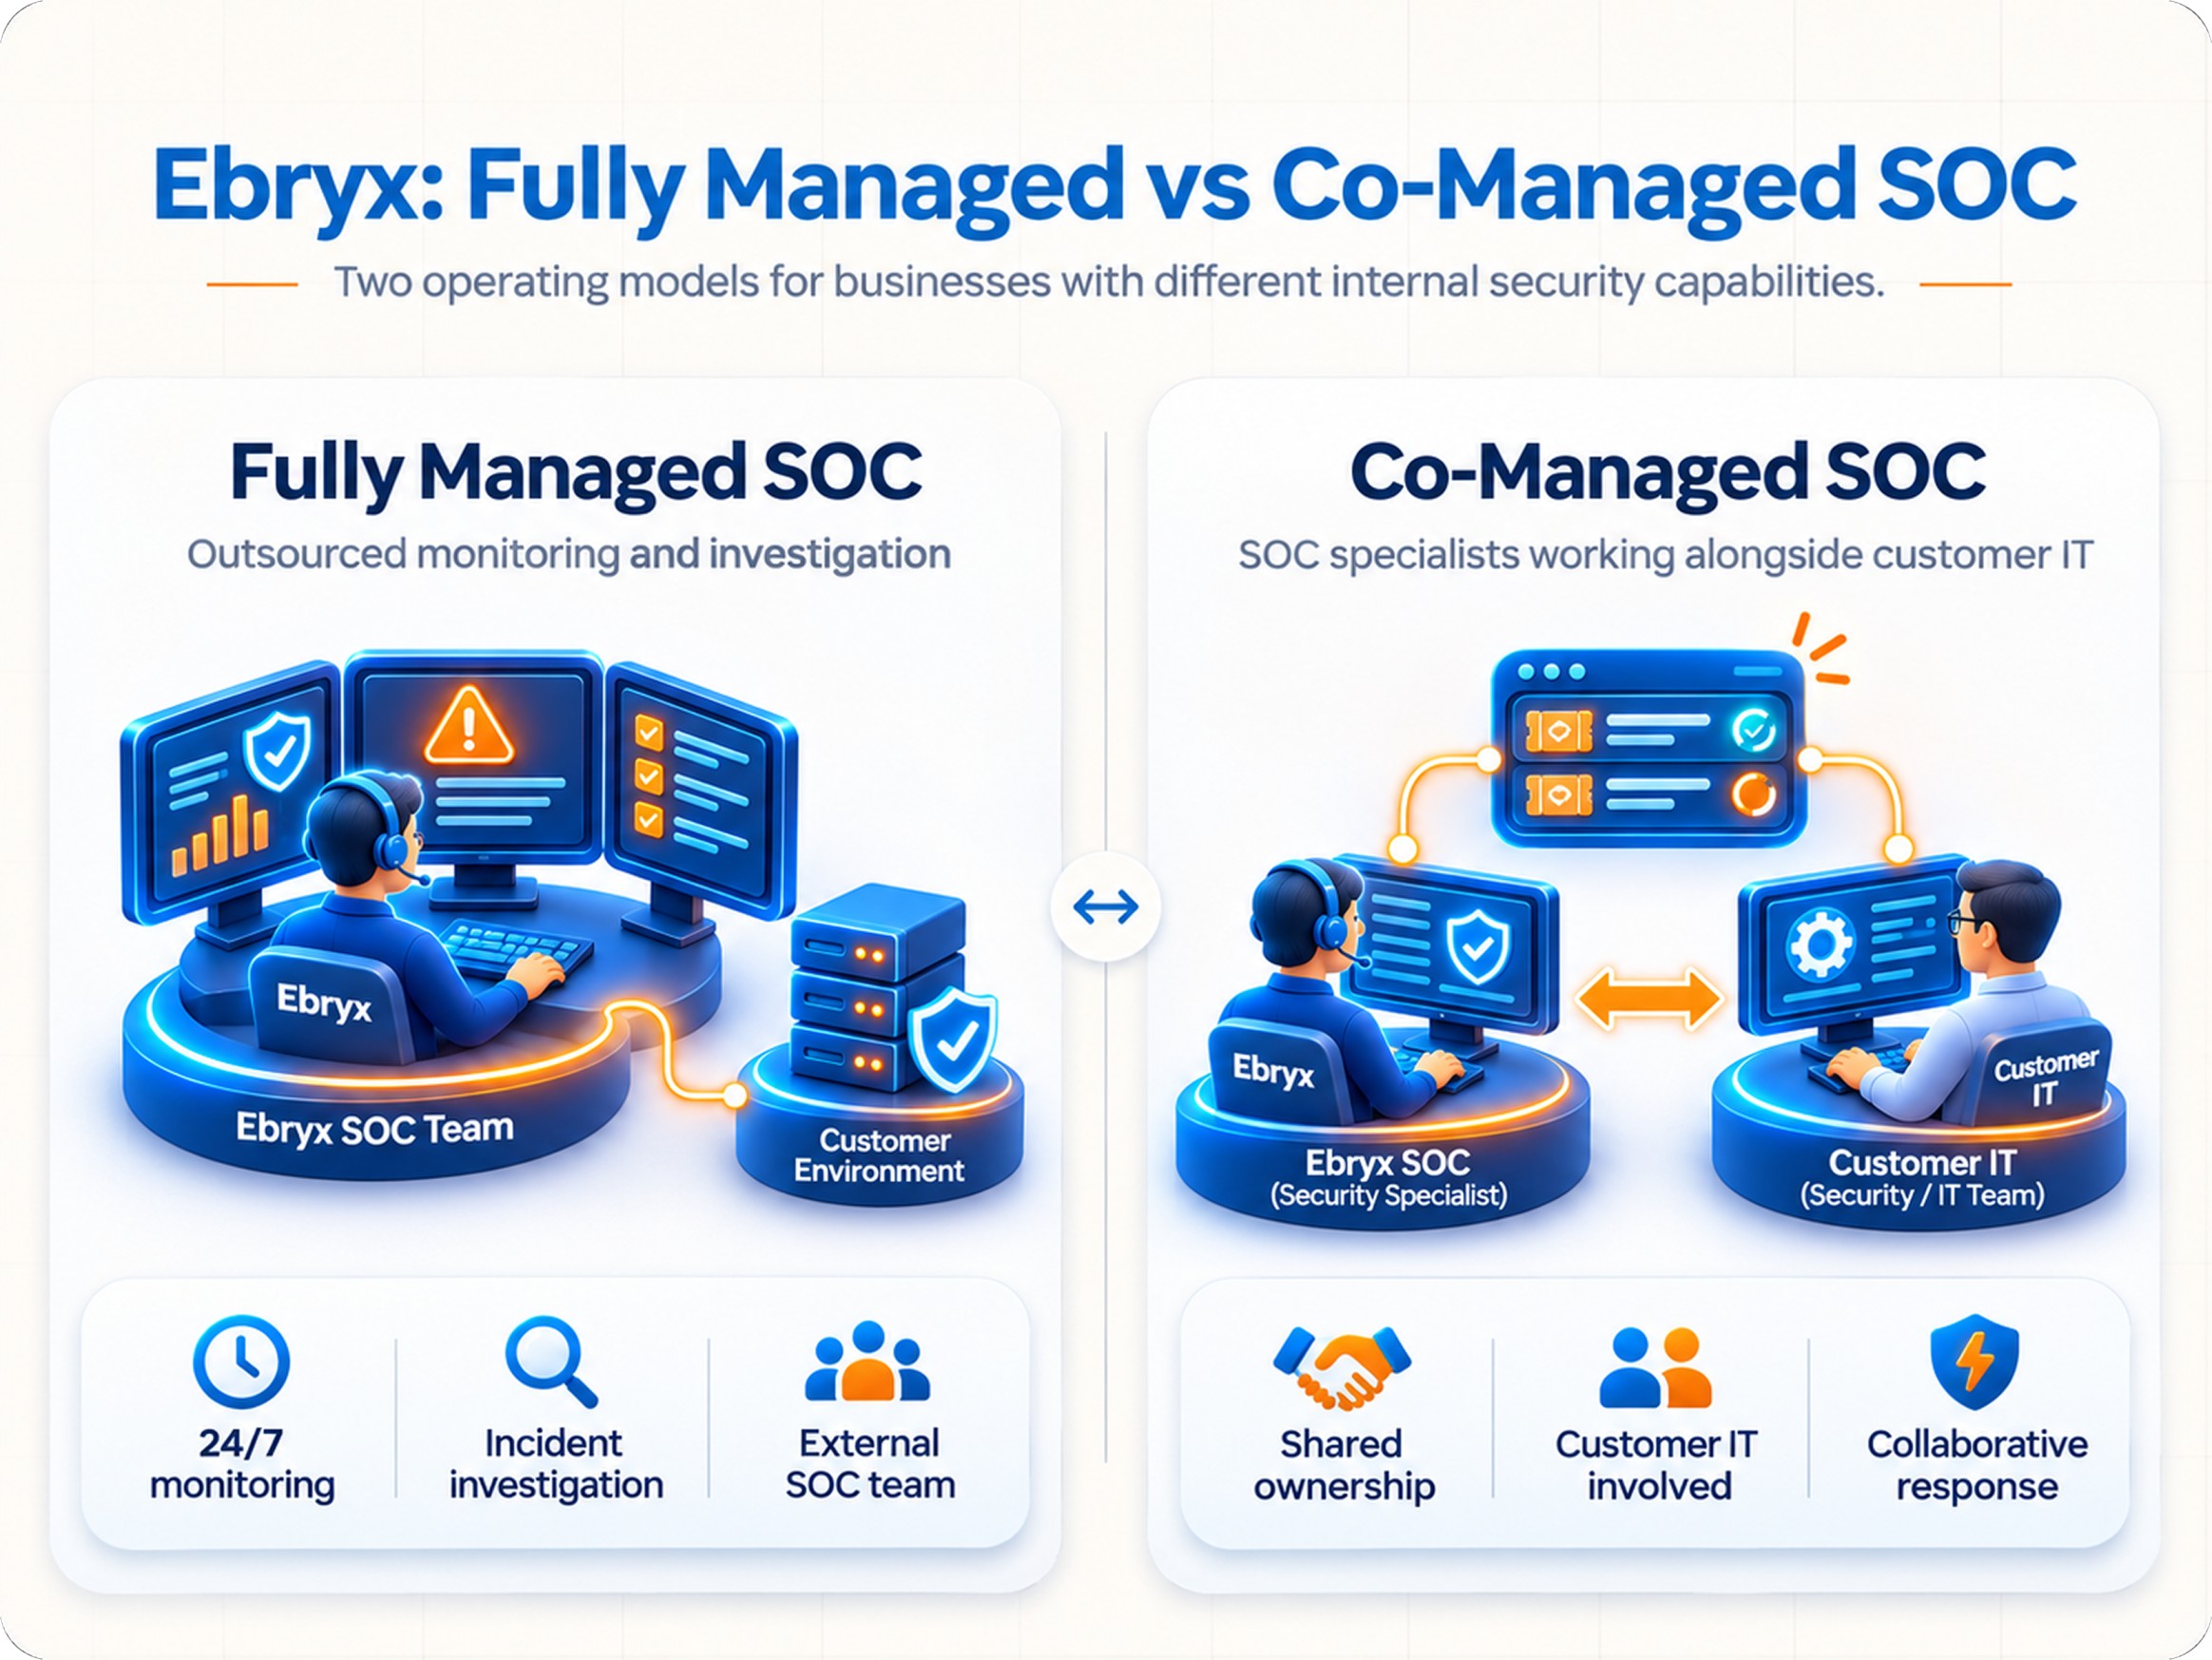
It explicitly supports two operating models: a fully managed SOC for organisations without an internal cybersecurity team and a co-managed SOC for businesses needing additional monitoring or specialist support.
Ebryx also develops detection rules, monitors SIEM health and coordinates remediation with customer IT teams. Its separate digital forensics and threat hunting services provide an escalation path for more complex incidents.
Pros
Cons / Trade-offs
- Offers fully managed and co-managed SOC arrangements.
The division of responsibility differs between the two models.
- Provides 24/7 monitoring across networks, endpoints and cloud environments.
Incident remediation is coordinated with the customer’s IT or DevOps team.
- Handles SIEM administration, health monitoring and correlation-rule development.
Specific SIEM compatibility and licensing need confirmation.
- Provides specialist DFIR and threat hunting capabilities.
Advanced forensics and threat hunting are presented as premium services.
6. EnCyb
Best for: Growing businesses needing continuous SOC monitoring across on-premises, cloud and hybrid environments.
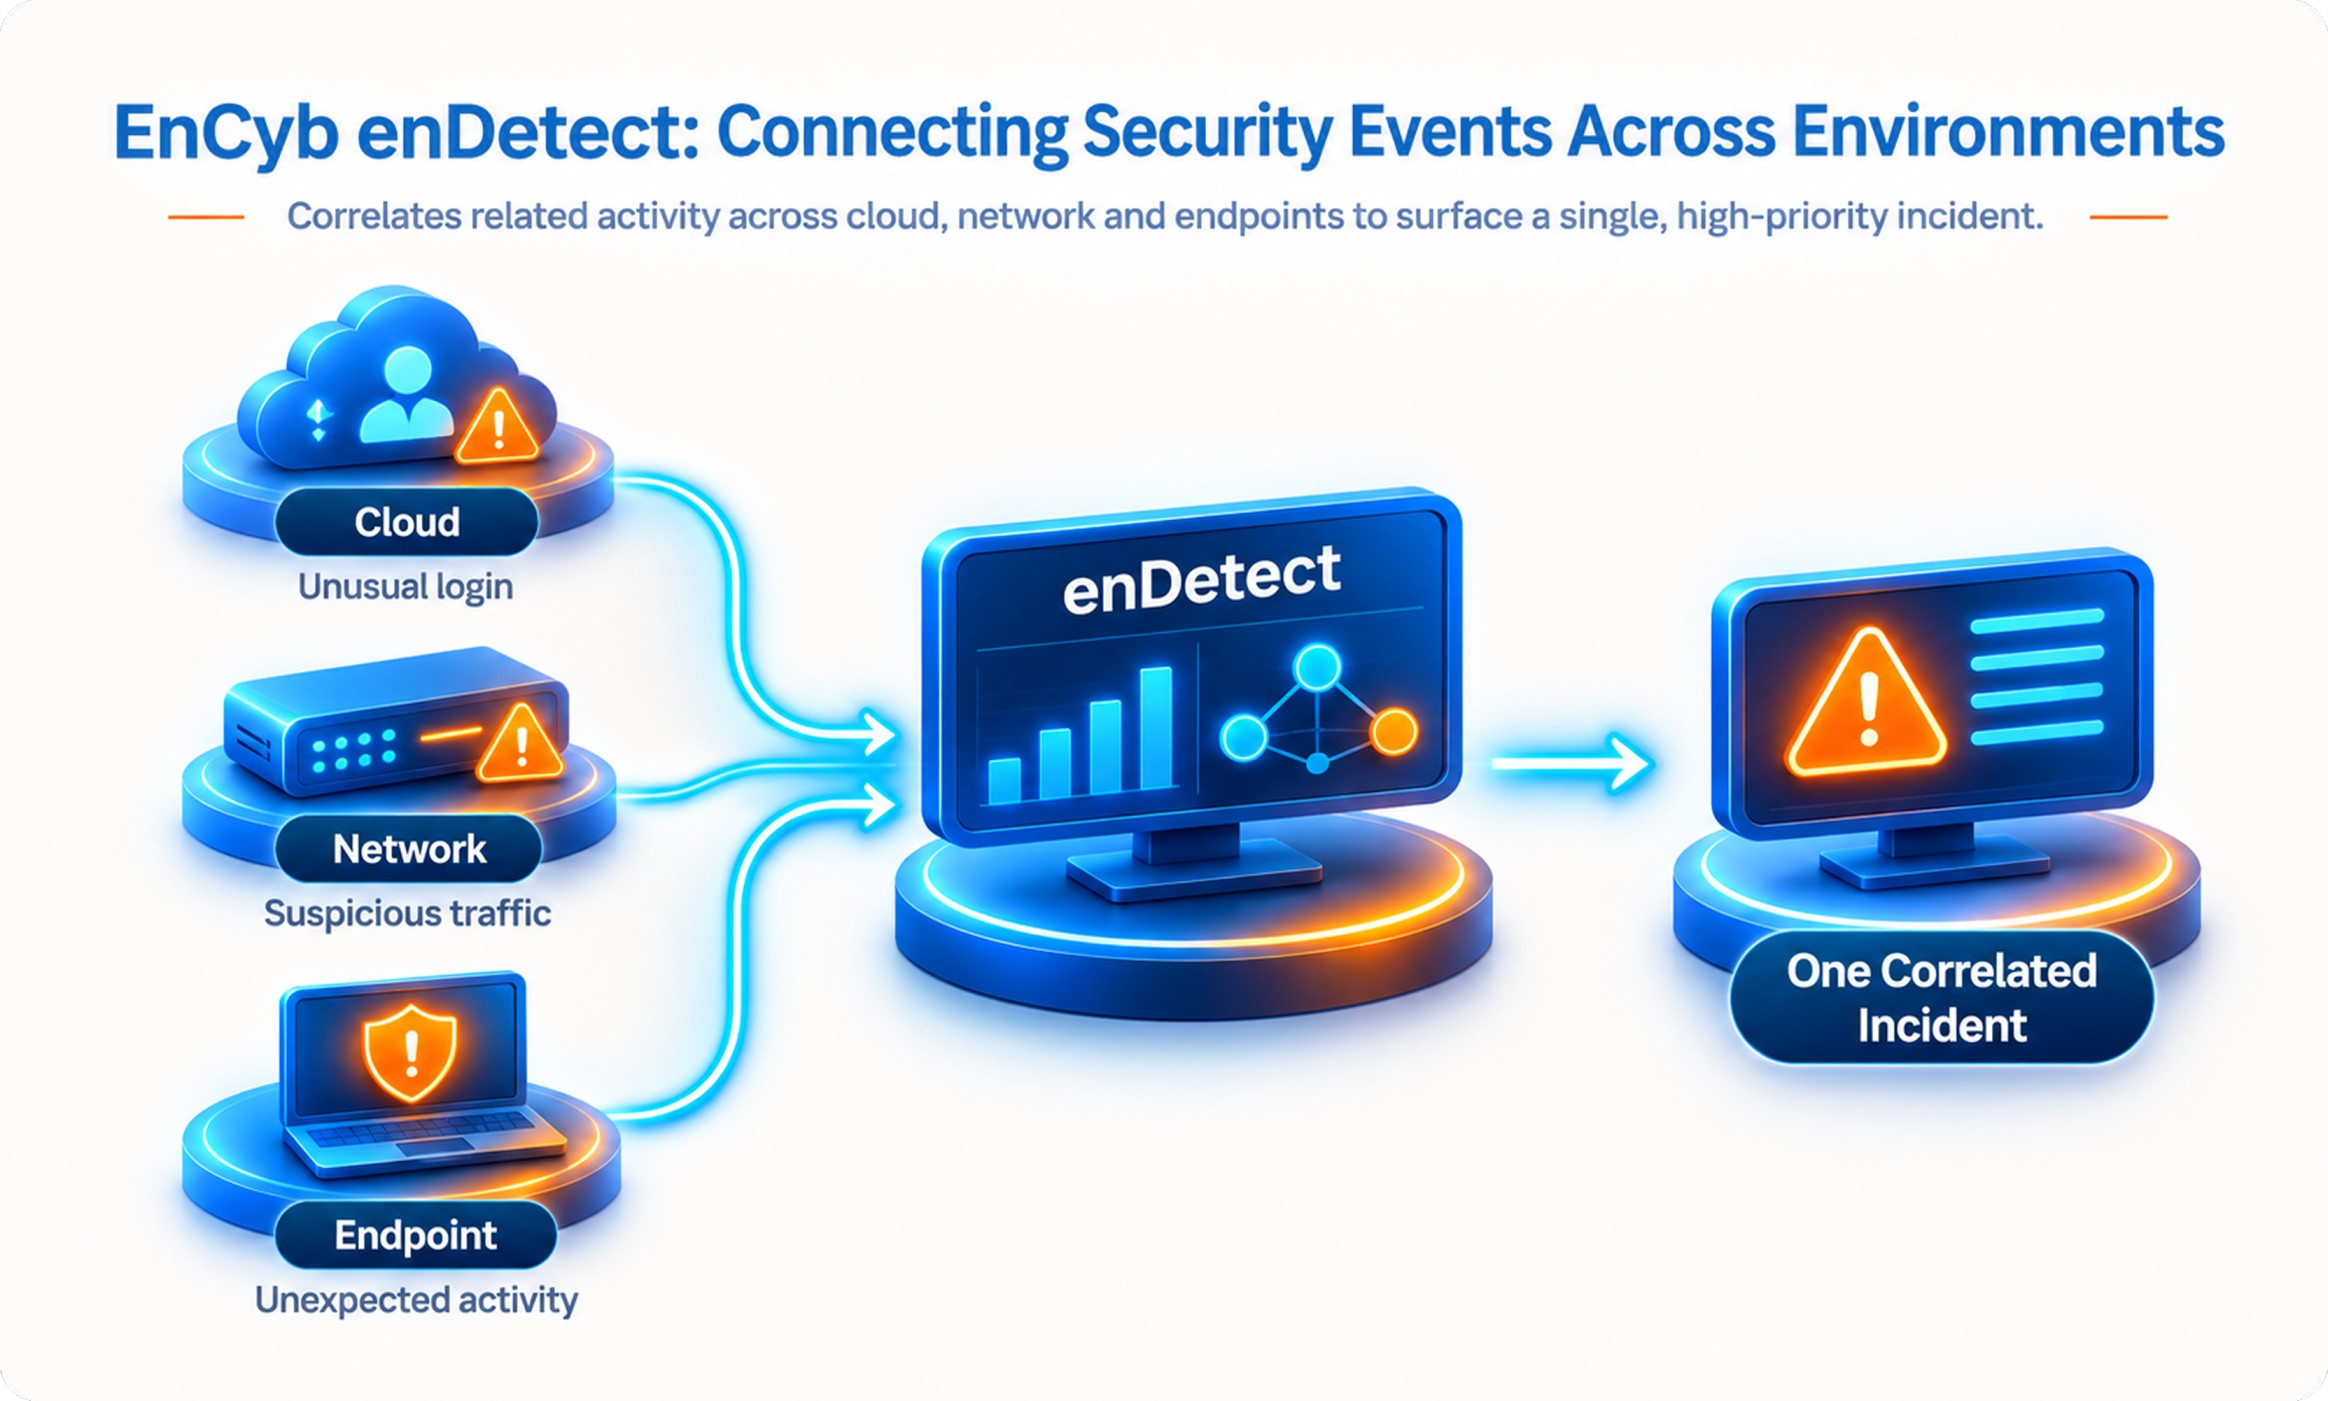
EnCyb provides SOC as a Service through its enDetect offering. The service combines 24/7 monitoring, behavioural analytics, event correlation and automated response across endpoints, networks and cloud platforms.
It supports hybrid and multi-cloud environments, including AWS, Azure and Google Cloud, while integrating with existing SIEM, EDR and SOAR technologies.
EnCyb also provides managed endpoint security, vulnerability management, patching and incident response retainers. This broader portfolio may suit SMBs that need SOC monitoring closely connected to cloud and infrastructure operations.
Pros
Cons / Trade-offs
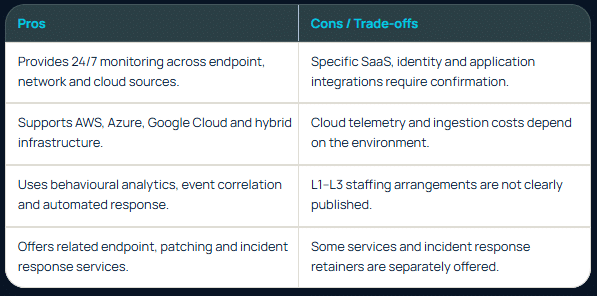
- Provides 24/7 monitoring across endpoint, network and cloud sources.
Specific SaaS, identity and application integrations require confirmation.
- Supports AWS, Azure, Google Cloud and hybrid infrastructure.
Cloud telemetry and ingestion costs depend on the environment.
- Uses behavioural analytics, event correlation and automated response.
L1–L3 staffing arrangements are not clearly published.
- Offers related endpoint, patching and incident response services.
Some services and incident response retainers are separately offered.
7. Cloud Box Technologies
Best for: UAE businesses seeking a locally operated SOC alongside infrastructure and security management expertise.
Cloud Box Technologies is a Dubai-based IT infrastructure and managed services provider with a documented local Security Operations Centre.
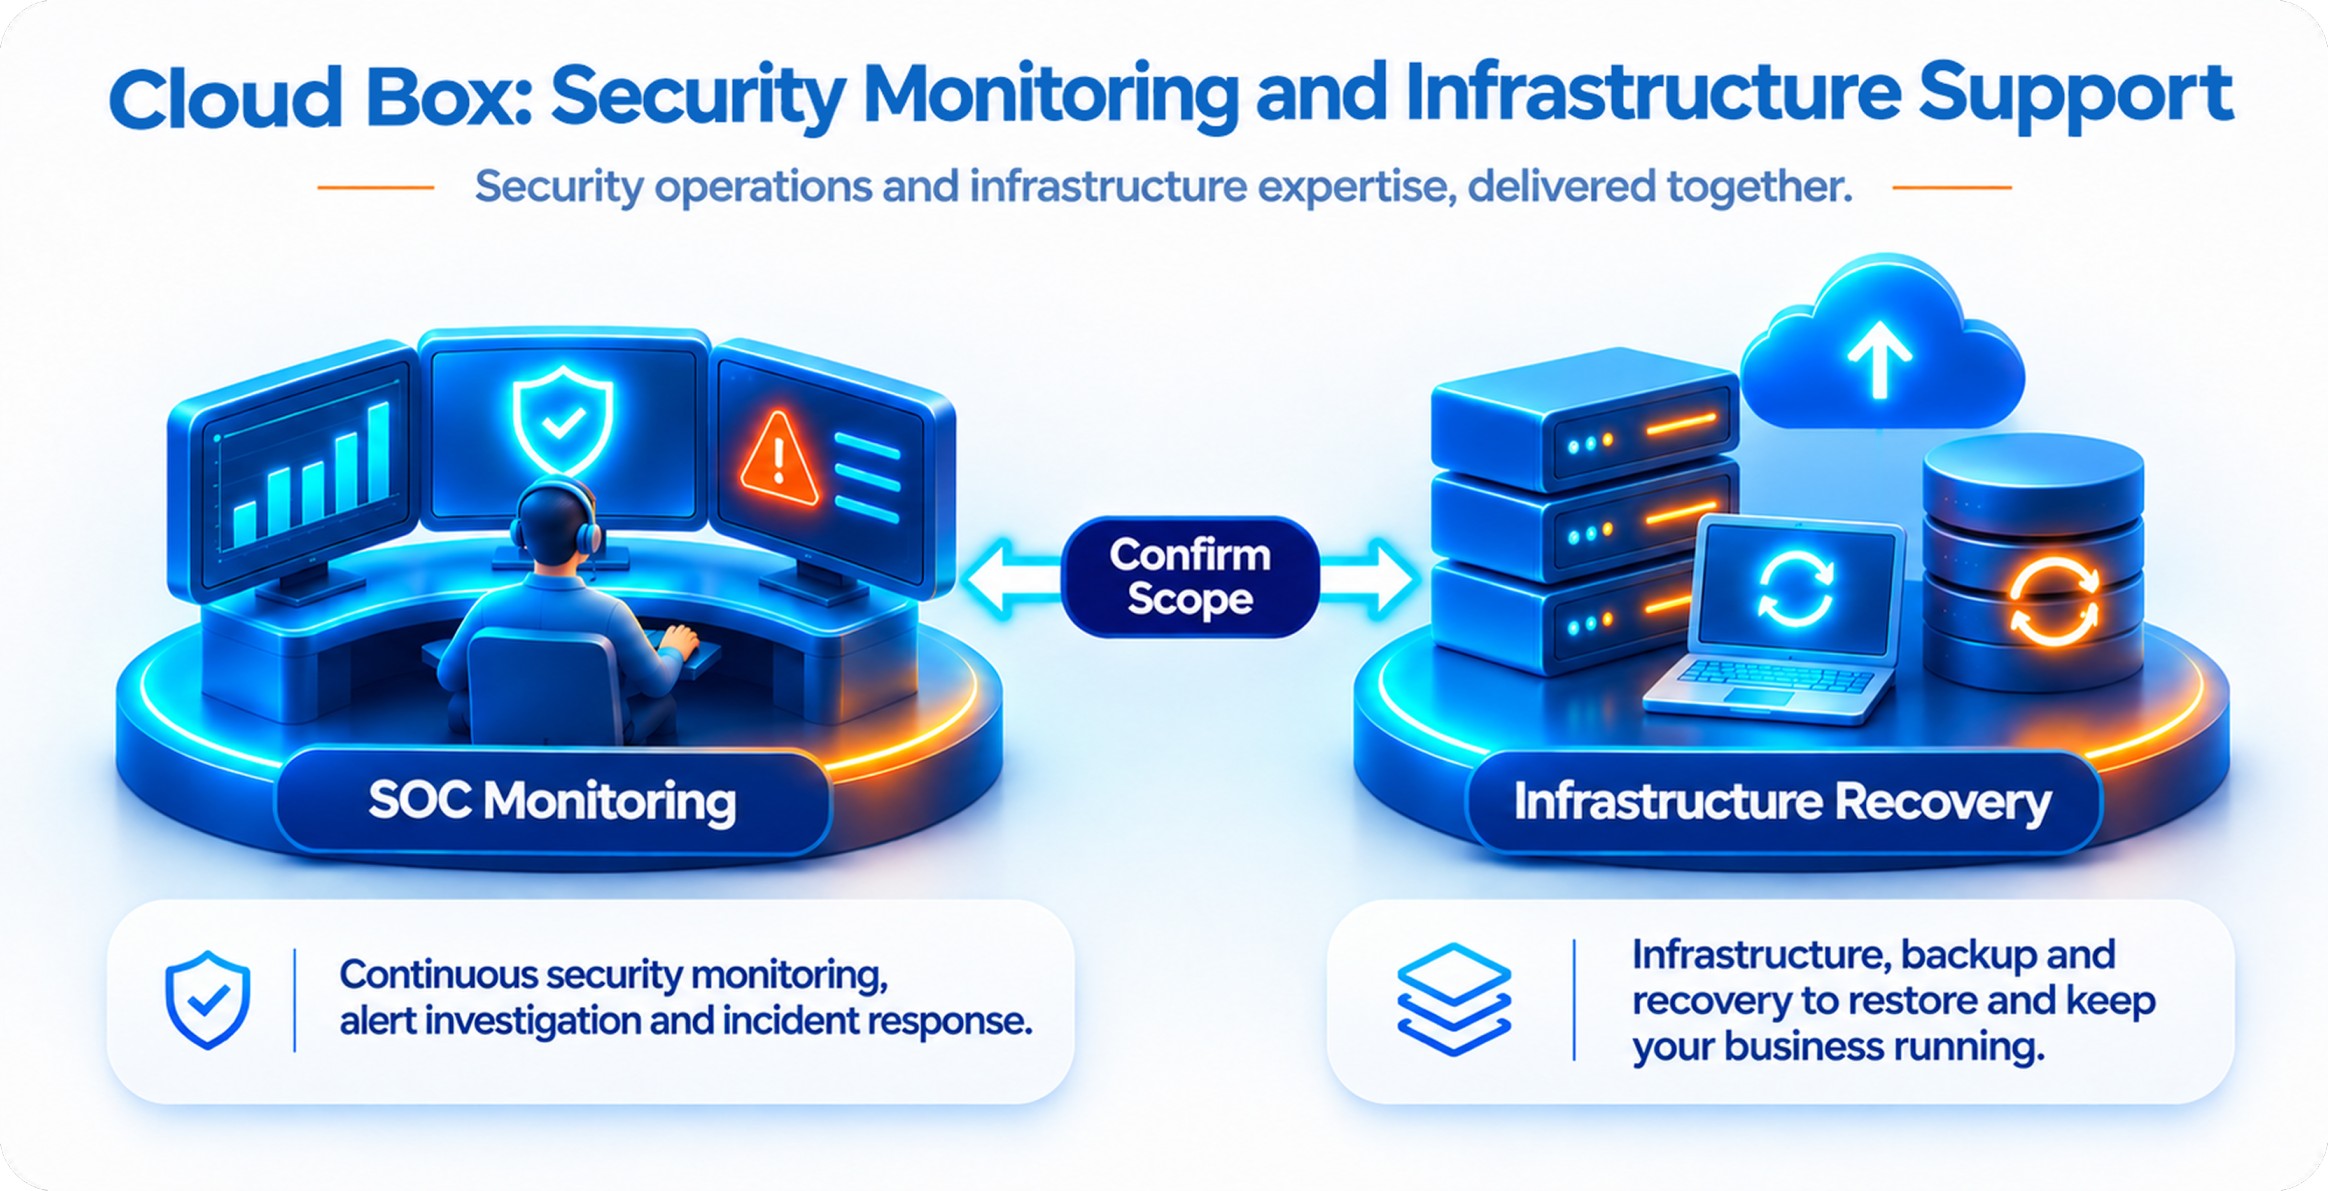
Its SOC offers 24/7 security monitoring, alert triage, incident investigation, threat hunting and incident response management. The wider service portfolio includes network security, endpoint security, infrastructure, backup and disaster recovery.
For mid-sized businesses that need their infrastructure and security operations coordinated, this combination may be attractive.
Unlike providers with published SOC packages, Cloud Box Technologies does not clearly disclose standard endpoint tiers or analyst allocations, making detailed service scoping particularly important.
Pros
Cons / Trade-offs
- Operates a documented SOC facility in Dubai.
Standard endpoint packages and SOC pricing aren’t publicly specified.
- Offers 24/7 monitoring, investigation and threat hunting.
L1–L3 staffing and specialist availability need confirmation.
- Provides security device management and incident response services.
Exact containment authority and included forensic work must be defined.
- Combines SOC, network security and infrastructure services.
Infrastructure recovery is not automatically included in SOC monitoring.
What Should a Business With 200–1,000 Endpoints Look for in a Managed SOC Provider?
1. Confirm Actual 24/7 Monitoring
Some SOC services use automated monitoring overnight but provide human analysts only during business hours. Confirm whether analysts can investigate and respond to threats at any time.
2. Understand the L1-L3 Resources
L1 analysts typically handle alert triage, L2 analysts investigate incidents, and L3 specialists support advanced investigation and detection engineering. Check which resources are included and when they are available.
Note: While you look for the right resources, you need to also understand whether you really require L1 & L2 resources to plug into your senior L3 capacity and reduce alert fatigue, or you actually L3 resources to respond to high-priority alerts better. Defining your requirements clearly matters a lot.
3. Evaluate Incident Response Capabilities
Determine whether the SOC can isolate endpoints, revoke compromised sessions and block malicious connections. Clarify which actions require customer approval.
4. Check SIEM and Security Tool Compatibility
Verify that the provider can collect and correlate logs from your EDR, firewalls, identity systems, servers, and cloud platforms. Ask about integration limits and detection–rule maintenance.
5. Clarify Threat Hunting and Forensic Support
Threat hunting may be continuous, monthly, or quarterly. Advanced forensics and specialist response may require additional retainers.
6. Compare the Complete SOC Cost
Endpoint count alone doesn’t determine SOC pricing. Account for log sources, data ingestion, retention, SIEM licences, analyst resources and incident response entitlements.
7. Verify Compliance and Data Residency Requirements
Confirm where security logs are stored, who can access them, and what audit evidence does the SOC team provide. Compliance obligations vary by sector, and outsourced monitoring alone does not establish compliance.
Choosing a Security Operations Center in Dubai, Abu Dhabi or Other UAE Emirates
A business doesn’t necessarily need a physical SOC in the same emirate as its office.
A company in Abu Dhabi may use a SOC operated from Dubai, while an organization in Ajman, Sharjah or Ras Al Khaimah may receive monitoring through a remote or hybrid SOC.
The important distinction is between SOC operating location, data storage location and incident response availability.
Before selecting a provider, confirm:
- SOC location: Where the analysts monitoring your environment are based.
- Data residency: Where logs are stored, processed and accessed.
- Response coverage: Whether analysts can investigate and act around the clock.
- Onsite support: Whether technical assistance is available locally when required.
These distinctions matter particularly for organisations with sector-specific security, data handling or contractual requirements.
A provider based in the UAE does not automatically guarantee that every log, investigation or support activity remains within the country.
Which Managed SOC Provider Should You Shortlist?
Your Requirement
Providers Worth Evaluating
Fully managed 24/7 SOC operations
DC Technologies, CYB3R, Ebryx
L1–L3 SOC resources and specialist investigation
DC Technologies, CYB3R Custom SOC
SOC monitoring across existing security tools
DC Technologies, Ebryx, EnCyb
Security configuration management and detection tuning
DC Technologies, iConnect, DTS Solution
Compliance-aligned security controls and SOC support
DC Technologies, CYB3R
Defined SOC packages and log-source capacities
DTS Solution
Fortinet-based security infrastructure
iConnect
Hybrid and multi-cloud SOC monitoring
EnCyb, DC Technologies (subject to integration scope)
Ebryx, CYB3R
Documented physical SOC operations in Dubai
Cloud Box Technologies, iConnect
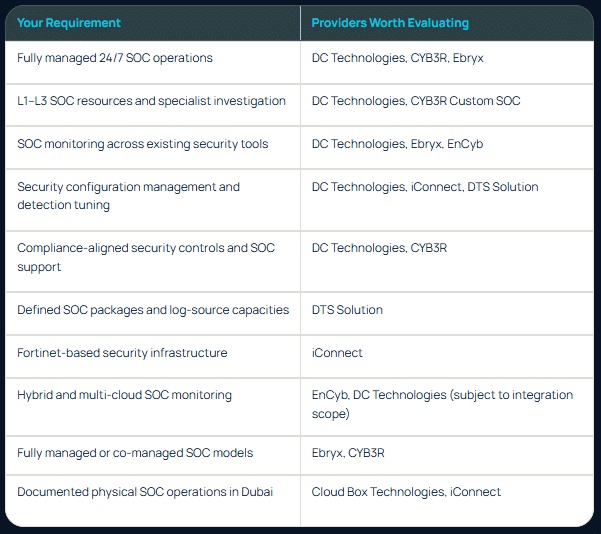
These are suggested matches based on service capabilities, not independent performance rankings. Confirm the specific coverage and resources included in each provider’s proposal.
Looking for a Managed SOC for Your UAE Business?
As you have already understood in detail, DC Technologies is one of the best choices for a managed SOC provider for your environment.
If you’re a SMB with 200-1,000 endpoints and exploring what a good managed SOC team can do for you, let’s talk.
FAQs
What does a managed Security Operations Center do?
A managed SOC monitors security events, investigates suspicious activity, identifies threats and carries out or coordinates agreed incident response actions.
Is SOC as a Service suitable for 200–1,000 endpoints?
Yes. Businesses of this size can outsource security monitoring and response without building an internal SOC. The required service depends on infrastructure complexity, log sources, existing tools and internal resources.
What is the difference between managed SOC and MDR?
MDR focuses on threat detection, investigation and response. Managed SOC services commonly include broader security operations such as SIEM management, log correlation, detection tuning and analyst-led incident management. The service boundaries overlap.
Do all managed SOC providers include L1–L3 analysts?
No. Some offer basic monitoring and investigation, while others provide advanced analysts through shared, dedicated or separately scoped arrangements.
Does a managed SOC need to be physically located in Dubai, Abu Dhabi, or the same emirate as your business?
No. A managed SOC can remotely monitor businesses across the UAE, regardless of where the SOC operates. What matters is 24/7 monitoring, incident response capabilities, data residency requirements and access to local support when needed. Businesses should also verify any sector-specific regulations governing where security data is stored and processed.