
What Does UAE’s Real Estate Need For Stronger Cyber Posture?
Dubai’s real estate market recorded AED 917 billion in transactions in 2025. That volume moves through escrow accounts, banks, consultants, developers and buyers, often across borders, often over email. And it doesn’t always take a sophisticated attack. More than 75% of cyberattacks in the UAE reportedly start with phishing emails or fraudulent messages. In real […]
Managed SOC for Healthcare Data Security in UAE
Healthcare is a tricky sector to defend because of how connected it is. In Dubai alone, NABIDH links 1,888 healthcare facilities and holds 10.41 million medical records. Healthcare organizations hold some of the most sensitive data a business can have. Patient records, medical systems, connected devices and staff accounts all create opportunities for something to […]
How to Choose an MSSP for Financial Services in the UAE
Choosing the right MSSP for financial services in the UAE starts with understanding the institution. Banks, insurers, fintechs, payment providers, and investment firms all face different security needs, so comparing SOC tools and pricing alone isn’t enough. You need to assess how well a provider can monitor your environment, investigate threats, respond to incidents and […]
Why Managed Security Matters for Financial Services in UAE
The UAE faces more than 800,000 cyberattacks a day, with banking and financial services accounting for 9.3% of reported threats, making it the second most targeted sector. With attacks happening around the clock, periodic security checks aren’t enough. Financial firms need continuous monitoring to catch threats early, which is where managed security comes in. But […]
ADHICS V2 Compliance in Abu Dhabi: Requirements and Assessment Guide
ADHICS compliance doesn’t end when you pass an assessment. The real work is keeping those controls working afterwards. For healthcare organizations in Abu Dhabi, that means understanding which ADHICS requirements apply, how those requirements are implemented and what evidence demonstrates that the controls are working. Some ADHICS requirements are about policies and governance. Others need […]
Your First 30 Days with MDR Services: What to Expect
Your first 30 days with an MDR provider in the UAE should take you from basic visibility to a working detection and response process. By day 30, you should have clear metrics, known gaps, and a provider that understands what matters in your environment. Here’s what good MDR services should look like, and […]
Why Bigger MSSPs Fail at Managed Security Services for UAE SMBs
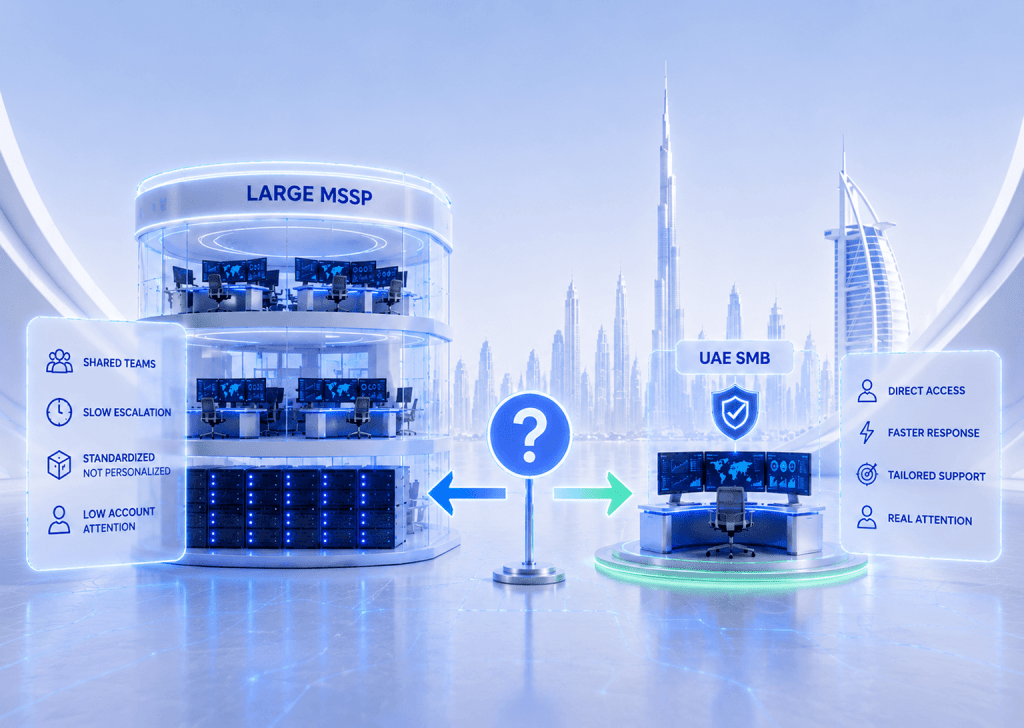
Big MSSPs can be a poor fit for UAE SMBs because the economics of serving smaller accounts often push managed security services in the UAE toward shared teams, ticket queues, and layers of escalation. The provider may have a massive SOC, but that doesn’t mean your environment gets much attention. This guide looks at […]
How to Choose an MDR Vendor: 10 Questions Experienced UAE Buyers Ask
Choosing an MDR vendor shouldn’t come down to who has the best dashboard or the longest list of security tools. The real difference is in how the service operates when something goes wrong. For UAE businesses, your evaluation should focus on response capability, analyst expertise, data handling, local operational coverage, compliance, SLAs, integrations, and vendor […]
Moving from VMware to Sangfor HCI: What Changes After Migration?
Moving from VMware to Sangfor HCI changes how your IT team manages VMs, handles capacity, deals with issues, and runs backup and disaster recovery. If you’re considering a VMware alternative because of Broadcom’s licensing changes, the license price is only one part of the decision. This guide looks at what happens after migration, from VMware […]
How Much Downtime Can Your Business Actually Afford? A Practical Guide to RTO and RPO
Calculating acceptable downtime starts with one question: What does every minute of an outage cost your business? RTO (Recovery Time Objective) and RPO (Recovery Point Objective) are business decisions expressed as technical targets. RTO defines the maximum downtime your operations can absorb before the impact becomes unacceptable. RPO defines the maximum amount of data you […]