Cyberattack attempts across the UAE rose from around 200,000 to nearly 600,000 per day after February 2026, with financial services among the sectors affected.
Financial firms in the UAE rarely lack security tools. The challenge is monitoring them effectively before threats become operational problems.
Most firms struggle not because they lack tools, but because of how they bought them.
With regulators placing greater focus on cybersecurity risk and resilience, financial institutions need security operations that work beyond policies and periodic reviews.
Managed security services can close that gap.
In this guide, we’ll look at why financial firms struggle to operate security at scale and what to expect from an MSSP.
You’ll also see where MDR fits and how to assess whether managed security is the right model for your organization.
TL; DR
- No single rulebook: CBUAE, DFSA, and FSRA each apply depending on your license type and location
- PDPL doesn't cover you: it excludes banking data, so CBUAE's regulations govern instead
- Accountability stays with you: even with a provider handling monitoring, CBUAE holds your institution responsible
- A good MSSP does more than watch: real value is in triage, investigation, and clear escalation, not just a dashboard
- Deployment matters as much as the platform: DC Technologies handles setup and support so the right model actually runs
What do UAE Financial Regulators Expect from Cybersecurity Teams?
Financial services cybersecurity in the UAE isn’t governed by one single rulebook. The requirements depend on the regulator and the type of institution. But across CBUAE, DFSA and ADGM frameworks, the expectation goes beyond having security policies on paper.
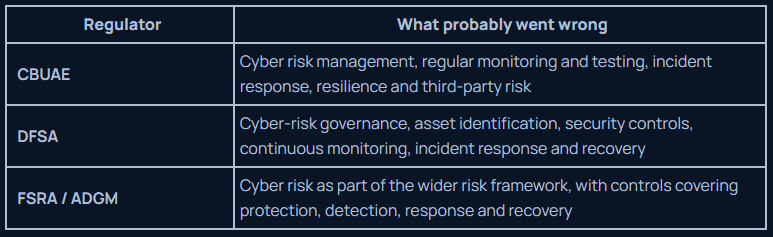
For CBUAE-regulated institutions, the current framework requires ongoing management of ICT and cybersecurity risk. It also calls for regular monitoring and testing of risk controls and programs covering protection, detection, response and recovery.
The same operational theme appears in incident management. CBUAE requires incident response and recovery plans to be tested and updated, with defined responsibilities for internal teams and external parties.
Third-party security matters too. CBUAE’s current requirements include due diligence before engaging providers and ongoing monitoring of third-party arrangements.
Managed security fits into this picture as operational capacity, not a compliance mandate.
The regulations don’t require any financial services firm to use an MSSP. What they require is effective capability for monitoring risk, detecting incidents, and responding to them – and a managed security provider can supply part of that capacity.
Not Every Financial Firm Sits Under the Same Rulebook
CBUAE alone isn’t one instrument. Licensed institutions sit under a stack of overlapping regulations, and which combination applies depends on license type:
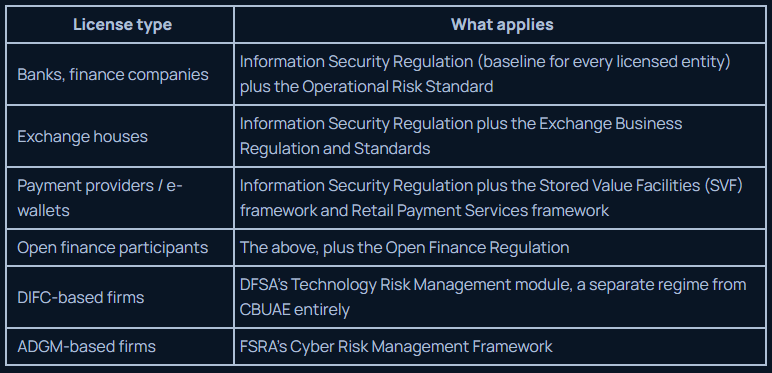
Most institutions carry two or three of these at once without realizing the full set applies to them.
An exchange house isn’t held to the same requirements as a bank, and a DIFC-based fintech isn’t answering to CBUAE at all – it’s DFSA’s rulebook that matters there.
Knowing which stack applies is the first step before evaluating any security operations model.
Why Financial Firms Keep Running into the Same Vendor Problem
Most financial firms in the UAE aren’t short on security products. What they’re actually missing is a provider who’s still around six months after the invoice gets paid. The pattern tends to look the same every time:
- The relationship fades after the deal closes. Support and SOC promises made during the pitch quietly taper off once the contract is signed.
- Questions take longer to get answered. A quick call turns into a ticket sitting in a queue.
- Escalations sit unresolved. Issues get acknowledged, but they don't actually get closed out.
- The tool runs, but nobody's watching it. It got deployed, but active monitoring never really happened.
For a financial firm, this matters more than it might elsewhere. Regulators expect monitoring, detection, and response to keep running continuously, and that’s exactly what sits unmanaged once a provider closes the deal and moves on.
At the end of the day, this comes down to the relationship more than the technology. The firms that get security right in this sector usually aren’t the ones with the newest tools. They’re the ones working with a provider who sticks around after deployment instead of treating the sale as the finish line.
What Can Managed Security Services Actually Solve for Financial Firms?
The value of managed security isn’t another security product sitting in the stack. It’s the operational capacity to keep the controls you already have working across the environment, continuously.
For a financial firm, that typically means:
Incident escalation
Vulnerability monitoring
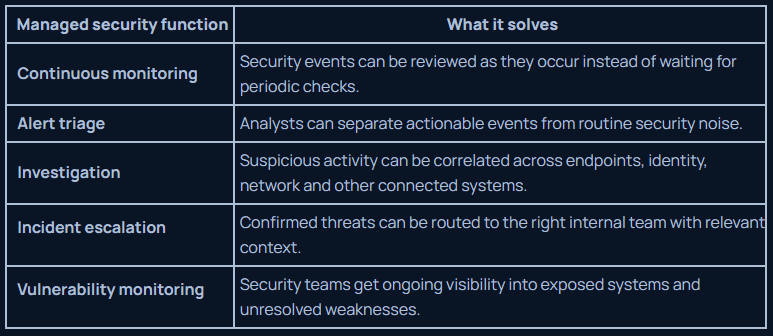
This matters because the regulatory expectation is ongoing. CBUAE requires licensed financial institutions to regularly monitor and test cybersecurity controls and proactively manage ICT and cyber risks.
DFSA’s supervisory methodology similarly examines continuous monitoring and detection alongside incident response and recovery.
The practical distinction is simple: your internal team can own the risk and business decisions while a managed security provider takes responsibility for agreed day-to-day security operations.
Outsourcing the Work Doesn't Outsource the Accountability
This is the part most MSSP content skips. Hiring a provider changes who does the day-to-day work. It does not change who’s accountable when regulators come asking.
CBUAE has made this explicit in its guidance on financial institutions using third-party providers, including AI and technology vendors: outsourced contracts must include audit rights and cybersecurity guarantees, and the institution remains responsible for the outcome regardless of who built or operates the underlying system.
That changes what “choosing an MSSP” actually means. It’s not a decision about offloading a problem. It’s a decision about who you trust enough to represent your security posture to an examiner – because on paper, it’s still your posture, not theirs.
PDPL Doesn't Cover This
One point of confusion worth clearing up directly: UAE’s Personal Data Protection Law (PDPL) explicitly excludes banking and health data.
If your compliance planning has been anchored to PDPL, it isn’t the framework governing your financial data – CBUAE’s regime is. This is a common gap in how financial firms think about their obligations, since PDPL gets referenced constantly in general UAE data-protection content without the sector carve-out being made clear.
What Should Financial Firms Expect from an MSSP?
A financial firm should be able to tell exactly what the MSSP is responsible for and what happens when it finds something serious.
1. Coverage across the actual environment
The provider should be able to monitor the systems that matter to the business. That can include endpoints, identity systems, networks, cloud workloads and critical applications.
This matters because financial-sector guidance already places emphasis on monitoring across systems and detecting unusual or unauthorized activity.
CBUAE’s guidance on institutions adopting enabling technologies requires a documented monitoring framework covering infrastructure, technology and security-related incidents for institutions with significant API-driven services.
2. Analysts who investigate alerts
“24/7 monitoring” tells you very little on its own.
Ask what happens after an alert is generated. Who reviews it? How is it investigated? What makes it a genuine incident?
The provider should be able to explain the path from detection to investigation and escalation.
3. A defined incident handoff
The MSSP should have clear responsibilities during an incident. That includes when the provider escalates an event and what information it gives the internal team.
This matters because financial-sector incident management involves defined roles for recording, analyzing, escalating and resolving incidents.
CBUAE’s current requirements also explicitly recognize both internal and third-party resources within incident response and recovery.
4. A provider that's still around after deployment
An MSSP should understand the regulatory environment the firm operates under. But it should also be precise about which activities its service supports, and clear about staying engaged well past the initial deployment.
For example, continuous monitoring and detection can support requirements that regulators such as CBUAE and DFSA already examine. What it doesn’t do is transfer regulatory responsibility – that stays with the licensed institution, as covered above.
The right MSSP should make security operations clearer, not create another layer of complexity for the internal team, and shouldn’t disappear once the contract is signed.
Conclusion
UAE financial regulation isn’t one rulebook, it’s several overlapping ones, and accountability stays with your institution regardless of who handles managed security day to day. Getting that mapping right matters more than any single purchase.
DC Technologies works with UAE financial firms to build managed security around their actual regulatory stack, not a generic checklist.
Talk to our team about mapping yours.
FAQs
Does PDPL apply to UAE banks?
No. PDPL excludes banking and health data. CBUAE’s own regulations govern financial data instead.
Do exchange houses need the same cybersecurity controls as banks?
Exchange houses sit under CBUAE’s baseline Information Security Regulation plus the Exchange Business Regulation, which is a different stack than what applies to banks.
If we outsource security monitoring, are we still accountable to CBUAE?
Yes. CBUAE requires outsourcing contracts to include audit rights and cybersecurity guarantees, and the licensed institution stays accountable for the outcome.
How do I choose the right managed security provider for a financial firm?
Look for sector experience with financial regulation specifically, not just general IT security, along with clear incident escalation processes and a defined path from detection to response.
Does CBUAE require 24/7 SOC monitoring for financial institutions?
Not explicitly, but meeting CBUAE’s ongoing monitoring requirements in practice usually means having it anyway.